How to become an ethical hacker and build a career
TL;DR
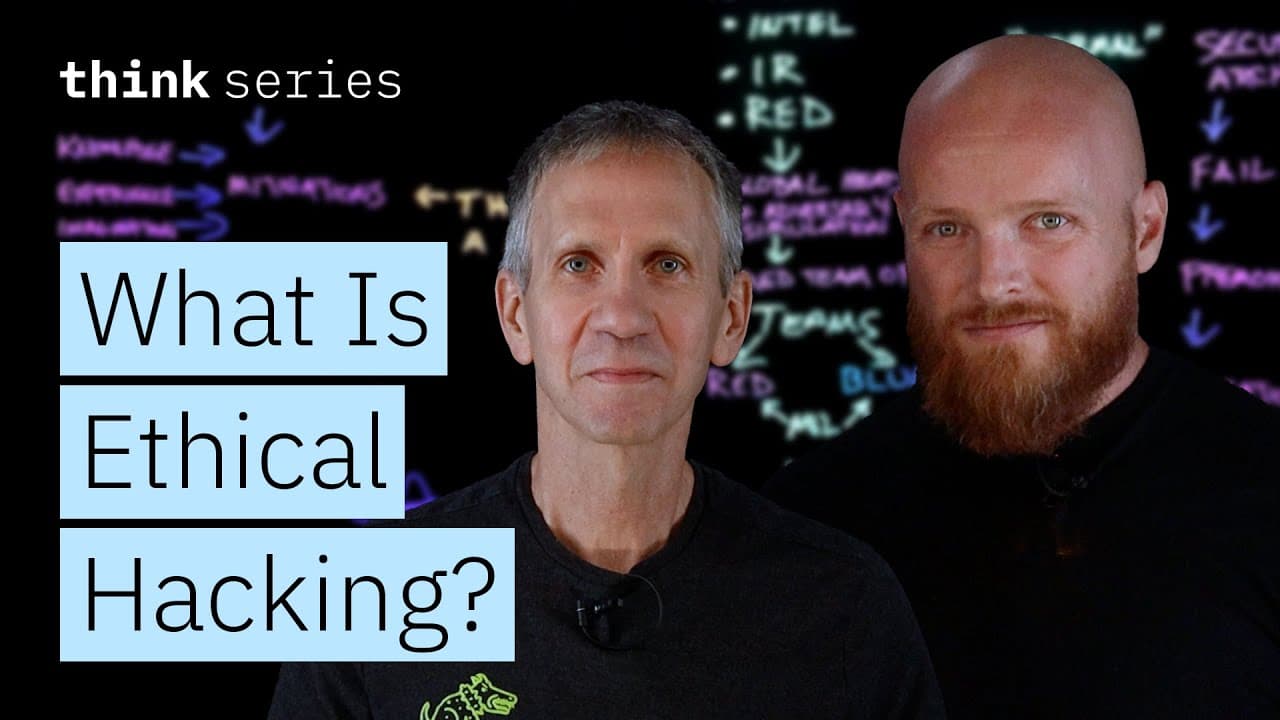
Ethical hacking is built on a three tier testing approach: vulnerability scanning, penetration testing, and red team exercises. It uses authorized testing to reveal gaps before attackers exploit them, distinguishing white hat from black hat roles and guiding a security career path from defense to adversary simulation.
Transcript
A colleague of mine once said that a normal IT architect envisions how a system will work, whereas a security architect envisions how a system will fail. Really turns out that a security architect has to do both. They have to figure out how the system will work, so that they can figure out what all the different failure cases might derive from that... Read More
Key Insights
- Ethical hacking uses a three layer testing pyramid: vulnerability scanning, penetration testing, and red team exercises to simulate real attackers and verify defenses.
- A security professional adopts a pre mortem mindset to identify failure scenarios early and design mitigations that prevent real incidents.
- Red team operators model adversaries such as nation state actors or ransomware groups to test and strengthen defenses against sophisticated threats.
- White hat hackers operate with permission to break into networks, while black hats act without authorization, highlighting the importance of legal and ethical boundaries in security work.
- The role of an ethical hacker blends tool aided automation with human expertise to locate and exploit vulnerabilities responsibly for remediation.
- Adversary simulation centers on proving whether a system can withstand a determined attack and how the organization would detect and respond to it.
- Blue teams focus on defense and incident response, while red teams play the attacker, creating realistic exercises that improve overall security posture.
- Career progression in this field includes moving from vulnerability scanning to hands on testing and finally leading adversary simulations, with ongoing opportunities for growth and higher impact.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: A real search query question about the video (e.g. 'How to...', 'What is...'). Question 1
Ethical hacking is a structured process that typically starts with vulnerability scanning to capture a broad view of potential weaknesses, using automated tools to collect data. This is followed by targeted penetration testing where skilled testers probe specific systems or applications to determine exploitable gaps and quantify risk, and finally red team exercises that simulate real world attacker behavior to validate defenses and response capabilities.
Q: What is the difference between red team and blue team roles?
Red teams act as the pretend bad guys testing defenses and determining how attacks could succeed, while blue teams consist of defenders who respond to incidents and strengthen security measures. The two work in tandem to provide a realistic assessment of an organization’s security posture, with the red team highlighting gaps and the blue team improving detection, containment, and recovery capabilities.
Q: Why is pre mortem analysis valuable in security architecture?
Pre mortem analysis helps security architects assume the system has already failed and backtrack to identify failure points and their root causes. This proactive thinking enables the team to design mitigations before an actual attack occurs, improving resilience by addressing vulnerabilities early and aligning defense with potential threat scenarios.
Q: What is the Global Head of Adversary Simulation responsible for?
The Global Head of Adversary Simulation leads a team of professional hackers who simulate adversaries to test networks and defenses. This role focuses on understanding attacker techniques, coordinating red team operations, and ensuring exercises accurately reflect real world threats to help organizations close gaps and improve security posture.
Q: How are white hat and black hat hackers distinguished?
White hat hackers are authorized to break into networks to identify and remediate vulnerabilities, while black hats operate without permission to exploit systems for malicious gain. The distinction centers on consent and intent, with white hats aiming to improve security and avoid legal consequences while black hats pursue illicit gains.
Q: What are the main components of an ethical hacking program?
An ethical hacking program comprises vulnerability scanning to map risks, penetration testing to verify exploitability and impact, and red team exercises to emulate sophisticated attackers. These components, supported by tools and skilled testers, provide a comprehensive view of security gaps and practical remediation steps.
Q: What career paths exist in ethical hacking according to the video?
Career paths in ethical hacking start with foundational roles like vulnerability assessment and security testing, then progress to more advanced positions such as adversary simulation lead or red team operator. Professionals gain experience across detection, response, and proactive defense, creating opportunities for leadership and specialization within cybersecurity.
Q: Why is permission important in ethical hacking work?
Permission is essential because it defines legal and ethical boundaries for testing activities. White hat engagements rely on explicit authorization to assess and improve security while avoiding legal penalties and reputational damage. This framework ensures testers can operate freely to identify risks without violating laws or harming systems.
Summary & Key Takeaways
-
Ethical hacking combines automated scanning with skilled testing to identify vulnerabilities before attackers do, then uses red team exercises to simulate true adversaries.
-
A security architect must think like a hacker, using pre mortems to anticipate failures and implement mitigations before incidents occur.
-
The career path in ethical hacking includes roles like vulnerability assessor, penetration tester, and adversary simulation lead, with a focus on defense, testing, and proactive security strategy.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator