How to identify Russia's top hackers and defend networks
TL;DR
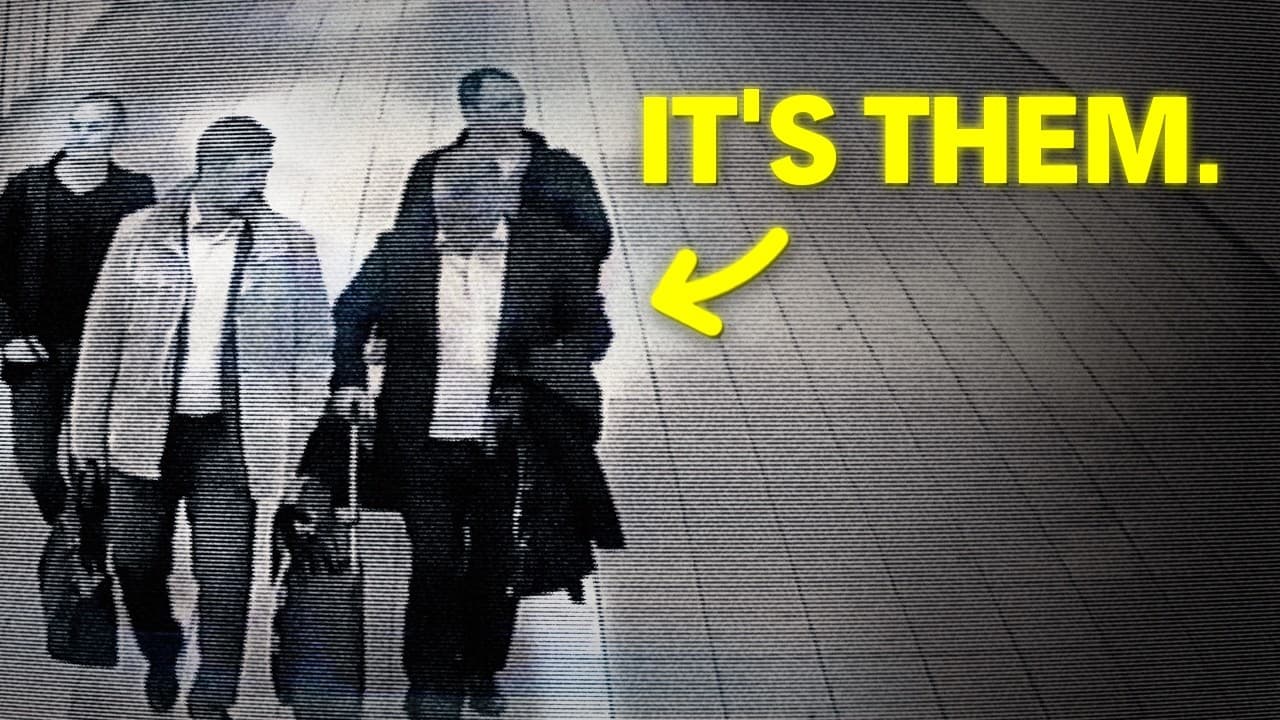
Russia's top hackers are elite units tied to the GRU that execute long term intrusions into government networks. The key to defense is early detection, rapid containment, and understanding attack patterns such as initial phishing like emails, stealthy malware like X Tunnel, and lateral movement within IT systems. The story shows how a German parliament breach unfolded and what investigators look for to interrupt similar campaigns.
Transcript
This is the story of the hunt for the world's most dangerous hackers. Prologue. The bears. Once upon a time, there were five bears. They all lived in Russia. Each one was different in the things they liked and in the things they did. But they shared one important trait. They were all seriously dangerous. There was the fancy bear, elegant, agile, an... Read More
Key Insights
- Hackers can gain administrator rights to digital master keys, enabling broad access across IT systems.
- AP28, also called Fancy Bear, is a Russian group tied to the GRU and known for patient, long term intrusions.
- Early warning from foreign security firms can prompt immediate response and containment measures.
- The attack timeline shows a slow realization by internal teams followed by rapid containment once recognized.
- Malware like X Tunnel acts as a continuous link for attackers to reenter networks when needed.
- Hacking campaigns in this case targeted political figures and government infrastructure to influence outcomes.
- Affected organizations require network shutdowns and selective restoration to prevent further data theft.
- Attribution to Russian intelligence is supported by the presence of specific tools, infrastructure, and known actor names.
- More videos from this channel:
- More from this channel: fern
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What is the significance of AP28 in the Bundestag attack
AP28, also known as Fancy Bear, is a Russian group associated with the GRU that conducted the intrusion into the German Bundestag. The group is characterized by stealth, patience, and the ability to stay embedded inside networks for extended periods. Their actions demonstrate how state sponsored cyber operations can compromise high level government systems and steal sensitive information.
Q: How did the initial infection occur in Claudia Height's case
In 2015, Claudia Height received an email that appeared official and referenced Ukraine, prompting her to click. The malware infected her computer and allowed attackers to move laterally inside the Bundestag IT infrastructure. The incident shows how a single deceptive email can open a path for a larger breach when internal processes fail to detect the threat.
Q: What does X Tunnel do in the attack story
X Tunnel is malware that creates a direct, continuous link into the network, allowing attackers to access the system whenever they want. It acts as a backdoor that lets intruders maintain presence inside the network, facilitating ongoing data access or further exploitation unless detected and removed.
Q: Why did the Bundestag network shut down
The security team decided to shut down the Bundestag network to prevent further data theft after detecting a major intrusion. This drastic step was necessary to cut off attacker access, stop the spread of malware, and begin a controlled clean up of the compromised environment, even though it caused disruption to parliamentary operations.
Q: What role did the BSI play in the response
The BSI deployed a special team to Berlin to analyze logs and determine the scale of the attack, whether the hackers were still inside, and what data might have been stolen. Their work was crucial for assessing risk, guiding containment, and coordinating with other agencies during the response.
Q: How is Fancy Bear described in relation to Russia
Fancy Bear is described as an elite unit of Russian intelligence services that conducts cyber operations for strategic goals. They are portrayed as fearless, patient, and capable of operating across borders, with the purpose of spying, exposing information, or causing disruption in line with Russia's political aims.
Q: What makes this cyber attack notable in German history
The Bundestag attack is depicted as one of the most serious cyber attacks in German history, provoking a large scale investigation and arrest warrants. The event highlighted weaknesses in national security, the complexity of modern cyber intrusions, and the need for robust government cyber defense and response coordination.
Q: What lessons about defense can be drawn from this story
Key defensive lessons include the importance of rapid incident response, timely escalation to security authorities, and the use of logs to trace attacker movements. Organizations should monitor for sophisticated means of initial access, isolate compromised segments quickly, and ensure strong credential management to limit attacker reach.
Summary & Key Takeaways
-
A cyber attack narrative explains how Russian intelligence linked hackers gained access to a national parliament and moved through the network, exposing how critical systems can be targeted and why rapid response matters.
-
The investigation traces malware, attack tools, and adversary behavior, highlighting the role of coordination between IT staff, national security agencies, and independent researchers in identifying and mitigating threats.
-
The documentary underscores defensive lessons such as monitoring for subtle intrusions, isolating infected devices, and securing administrative credentials to reduce attacker dwell time in networks.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from fern 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator