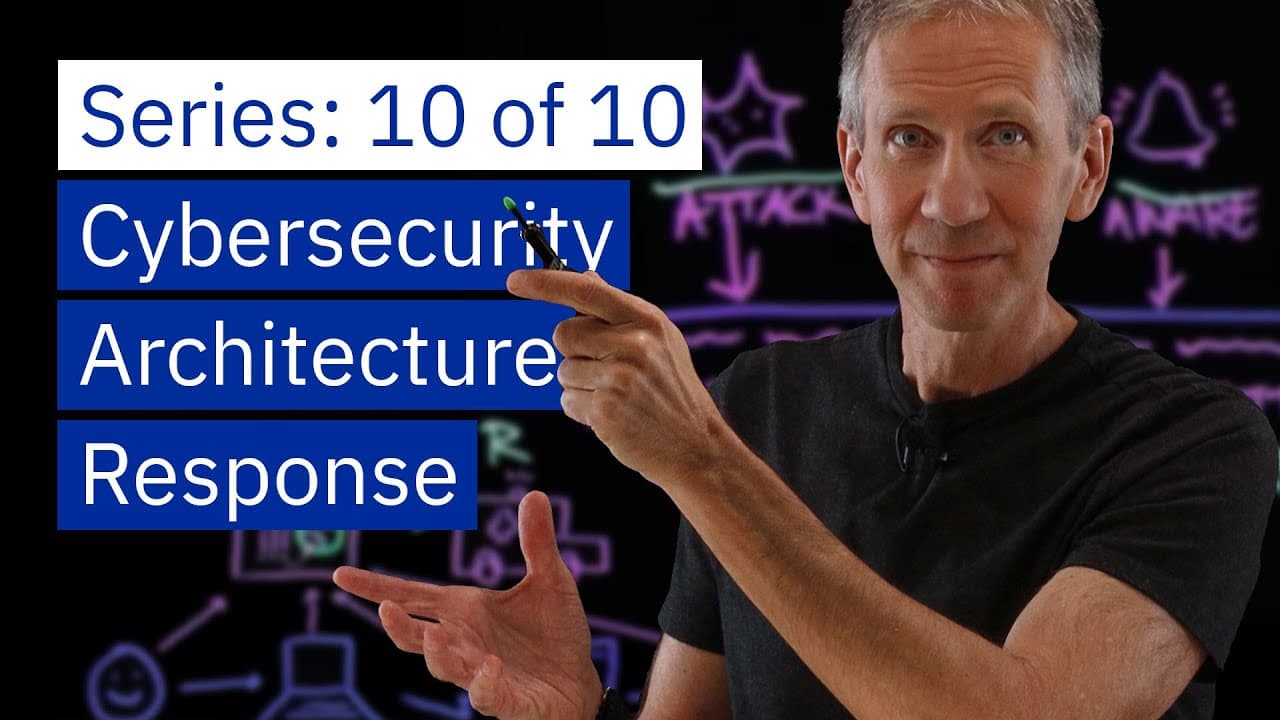
How Does Incident Response Work in the Cybersecurity Architecture Series?
TL;DR
Cybersecurity incident response works by triaging alerts, prioritizing real attacks, and remediating damage through blocking, patching, and restoring systems. The cited mean-time-to-contain is roughly 70 days after a breach is identified, while SOAR uses orchestration and automation to shorten that period and make response more repeatable. Read on to understand the SOC, key response metrics, and the shift from manual incident response to SOAR.
Transcript
Remember that equation. This we covered in the last episode of the Cybersecurity Architecture series. Welcome back. This was about security equals prevention, plus detection, plus response. This is basically what we're doing in security. And we talked about at the very beginning of the series some security principles and roles and things like that,... Read More
Key Insights
- Security equals prevention plus detection plus response. Prevention controls span identity and access management, endpoint, network, application, and data domains, detection does the monitoring, and response handles what happens after a problem is discovered.
- Mean-time-to-identify (MTTI) averages roughly 200 days according to the Ponemon Institute's Cost of a Data Breach survey, meaning attackers sit inside a victim's environment for about 200 days before the breach is even noticed.
- Mean-time-to-contain (MTTC) is on the order of 70 days, representing how long it takes once aware to control the damage, remove the attackers, and get back to operation. This is the response portion.
- These MTTI and MTTC numbers stay roughly the same over the years despite more tooling and understanding, showing the industry has not been effective at reducing the time to identify and contain breaches.
- The Security Operations Center (SOC) is a centralized team that monitors information sent up from each domain, detects anomalous behavior and alerts, correlates it, and then responds to what it finds.
- Traditional incident response (IR) is largely a manual process that relies on heroes and experts whose knowledge lives in their heads. It does not scale well and is not necessarily repeatable, but it cuts breach cost when done well.
- SOAR stands for security orchestration, automation, and response. It aims to make things as automated as possible to reduce containment time, contrasting with the traditionally manual IR approach.
- Dynamic playbooks guide analysts by predetermining that when you see a given signal you run a given routine, with subsequent steps depending on prior results, so less experienced people can follow guidance instead of needing all the expertise themselves.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How does incident response work in cybersecurity?
Incident response begins after defenders discover a security problem. A Security Operations Center triages incoming alerts, prioritizes confirmed attacks, and remediates them by blocking threats, shutting down affected components, applying patches, adding controls, and restoring operations.
Q: What is the security equation used in the Cybersecurity Architecture series?
The series defines security as prevention plus detection plus response. Prevention uses controls across identity and access management, endpoints, networks, applications, and data; detection monitors for problems; and response controls damage after discovery.
Q: What is mean-time-to-identify, or MTTI?
Mean-time-to-identify is the period between an attacker entering an environment and defenders becoming aware of the breach. The Ponemon Institute's Cost of a Data Breach survey is cited as placing the average at roughly 200 days.
Q: What is mean-time-to-contain, or MTTC?
Mean-time-to-contain measures how long defenders take after discovering a breach to control the damage, remove the attackers, and resume operations. The transcript puts it on the order of 70 days and identifies reducing that period as a central response goal.
Q: What does a Security Operations Center do during incident response?
A Security Operations Center, or SOC, is a centralized team that monitors information from multiple security domains. It detects anomalous behavior and alerts, correlates the available information, and coordinates the response.
Q: What are triage and remediation in incident response?
Triage determines whether an alert represents a real attack or noise, how significant it is, and where it belongs in the response priority. Remediation fixes the problem through measures such as blocking, shutting systems down, applying software patches, stopping data leakage, and restoring operations.
Q: What is the difference between traditional incident response and SOAR?
Traditional incident response is largely manual and depends on experts whose knowledge and judgment may not scale or produce repeatable results. SOAR emphasizes security orchestration, automation, and response to automate as much of the process as possible and help reduce containment time.
Q: Why are automation and orchestration important in cybersecurity response?
The cited mean-time-to-identify and mean-time-to-contain figures have stayed roughly constant over the years despite increased tooling and understanding. Automation and orchestration aim to make response less dependent on manual expertise, more repeatable, and faster at containing incidents.
Summary & Key Takeaways
-
The Cybersecurity Architecture series frames security as prevention plus detection plus response. Prevention covers identity, endpoint, network, application, and data controls; detection monitors for problems. This final episode focuses on response: once a breach is discovered, how the damage gets controlled and the attackers removed.
-
Attacks begin with reconnaissance, then damage. Mean-time-to-identify averages about 200 days and mean-time-to-contain about 70 days per the Ponemon Cost of a Data Breach survey. These numbers stay roughly constant over the years despite better tooling, showing the industry struggles to shrink them.
-
The SOC triages alerts to separate real attacks from noise and rank significance, then remediates by blocking, patching, and restoring systems. Modern SOAR adds automation, case management, enriched artifacts and indicators of compromise, and dynamic playbooks to guide analysts and reduce containment time.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator