How to securely enable CORS for cross origin APIs
TL;DR
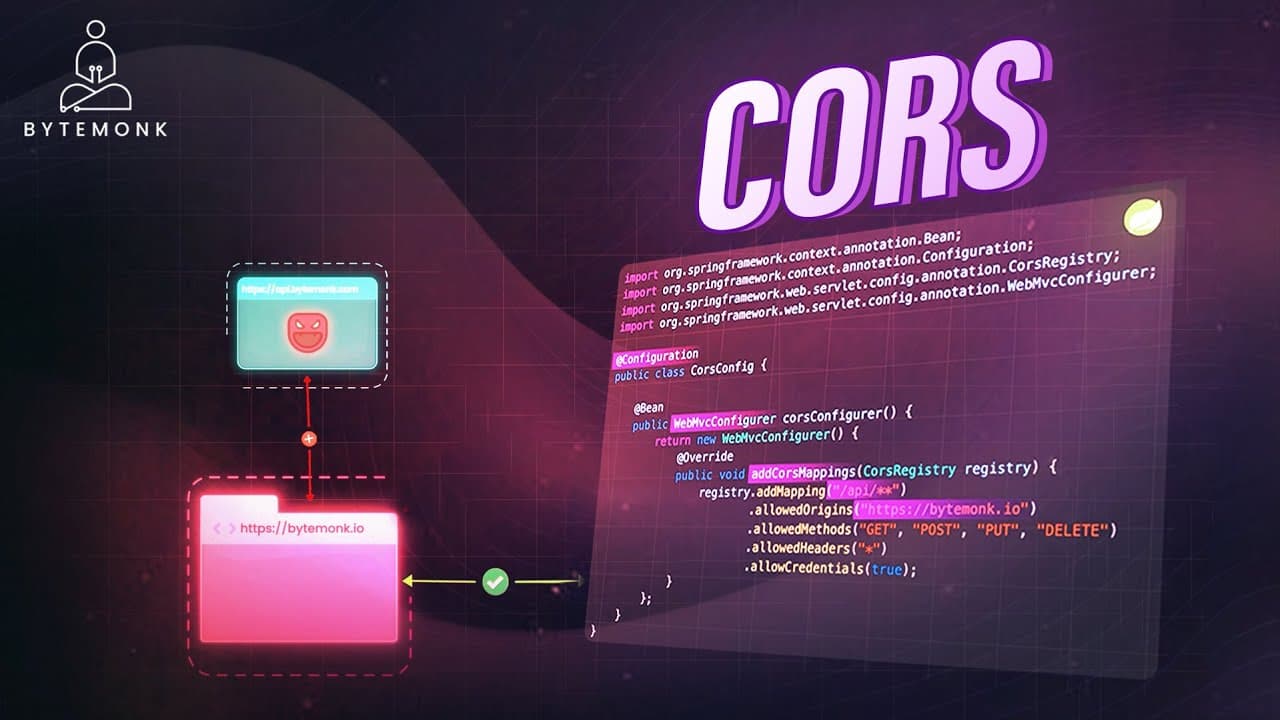
The browser enforces the Same Origin Policy to block cross origin requests by default. CORS uses HTTP headers from the server to indicate which origins are allowed. Simple requests often work without preflight, while complex requests trigger a preflight OPTIONS check before the real request. Backend or proxy fixes are common ways to enable secure cross origin access.
Transcript
if you have ever built a web app that fetches data from another server chances are you have encountered course at least once but don't worry by the end of this you'll know exactly what's going on why course exist and how to handle it like a pro let's start with a simple question why can't your browser Just Fish data from any website anytime however... Read More
Key Insights
- The Same Origin Policy restricts cross origin API requests to protect user data and prevent malicious site actions.
- CORS relies on server side Access-Control-Allow-Origin headers to authorize cross origin access for a requesting origin.
- Simple requests use GET, POST, or HEAD with standard headers and may not trigger a preflight, allowing smoother cross origin interactions.
- Preflight requests are OPTIONS calls used to verify permissions when the request uses non standard methods or custom headers.
- If the server does not authorize the origin or headers, the browser blocks the request and reports a CORS error.
- Configuring the backend server to allow cross origin requests from specific origins or all origins is a common solution.
- Proxy based workarounds can forward requests to appear as same origin when backend changes are not possible.
- Browser extensions for CORS are useful for development and testing but should not be used in production.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What is CORS and why is it needed for cross origin requests?
CORS stands for Cross Origin Resource Sharing and it is a mechanism that allows servers to specify who can access their resources from a different origin. It exists to prevent malicious websites from reading sensitive data from another site without permission. By sending appropriate headers, a server can permit or deny cross origin requests from particular origins.
Q: How does the Same Origin Policy affect browser requests?
The Same Origin Policy restricts a web page loaded from one origin from making requests to a different origin unless the target server explicitly allows it. This helps protect user data by preventing unauthorized access across domains, protocols, or ports, ensuring that only trusted origins can interact with a given API.
Q: What is a simple CORS request?
A simple CORS request uses the GET, POST, or HEAD method and does not include custom headers or non standard content types. In these cases the browser may not perform a preflight check and will rely on the server header if the response is allowed, allowing the data to be fetched directly.
Q: What triggers a preflight request in CORS?
A preflight request is triggered when the actual request uses a non standard HTTP method like PUT or PATCH, or includes custom headers such as Authorization, or uses a non standard content type. The browser sends an OPTIONS request to check permissions before sending the real request.
Q: What header does the server send to allow cross origin access?
The server sends the Access-Control-Allow-Origin header to indicate which origins are permitted to access the resource. If the header is present and allows the requesting origin, the browser will proceed with the actual request; if not, it blocks the request.
Q: What are common ways to fix CORS issues on the backend?
Common fixes include configuring the server to allow cross origin requests from specific origins, and specifying allowed HTTP methods and headers. In frameworks like Node.js or Spring Boot, you can set global CORS policies, enable credentials, and ensure security configuration respects the CORS rules.
Q: What is the role of proxies in solving CORS during development?
Proxies forward requests to the backend so they appear to originate from the same origin as the frontend, bypassing cross origin restrictions for testing. This helps developers test API responses without changing server configurations, but should not be used as a production solution.
Q: Why is CSRF different from CORS and why is it mentioned here?
CSRF is a separate security issue where an attacker tricks an authenticated user into making unintended requests, potentially transferring funds or performing actions. CORS does not protect against CSRF; CSRF tokens and cookie safeguards are needed to mitigate that risk, which is why it is noted for future coverage.
Summary & Key Takeaways
-
A practical overview of why CORS exists and how the browser enforces it, focusing on the difference between same origin and cross origin requests and the role of HTTP headers.
-
An explanation of how preflight requests work with complex methods and custom headers, including when the browser sends an OPTIONS request before the actual API call.
-
A look at common remediation strategies for CORS issues, including backend configuration, front end workarounds, and the use of proxies for development and testing.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from ByteMonk 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator