How to Configure ProxyChains on Kali Linux
TL;DR
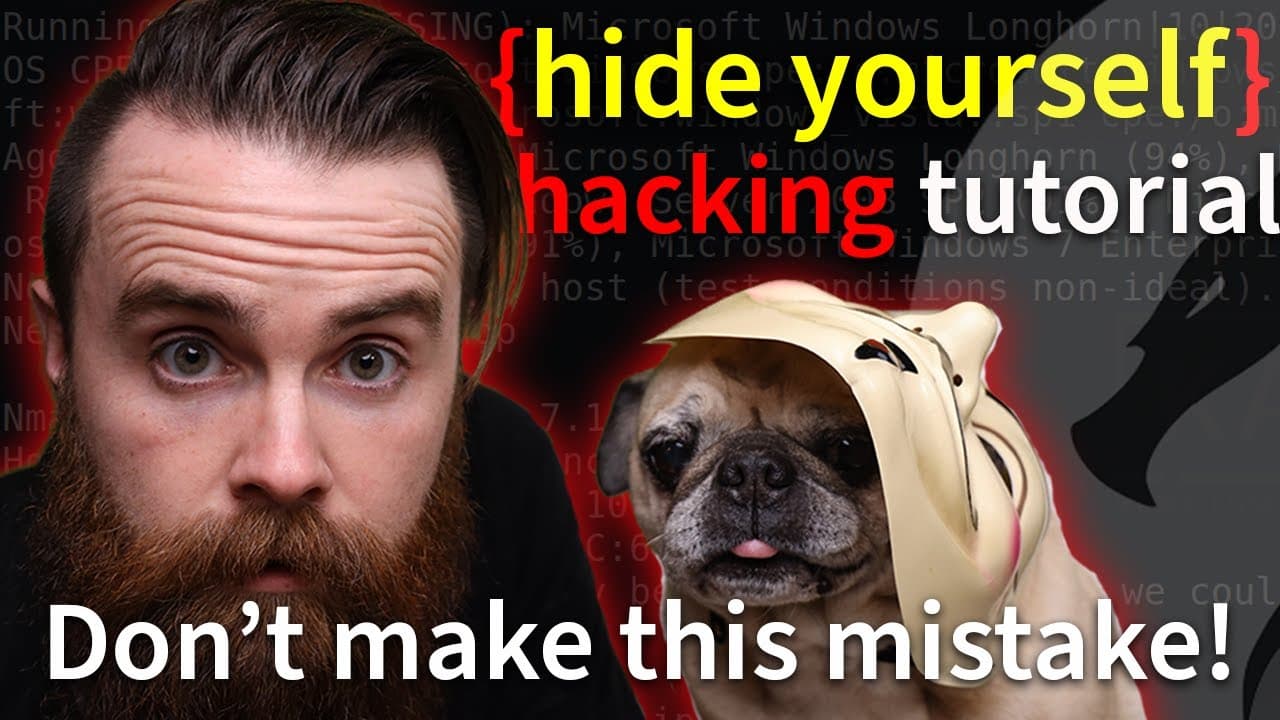
Configure ProxyChains by enabling dynamic chaining, keeping proxy DNS active, and adding proxy servers with their type, IP address, and port to the configuration file. Prefix supported commands with proxychains, then verify the route through a browser and public IP search. Use these techniques only for ethical hacking with explicit permission, because proxy chains do not guarantee anonymity.
Transcript
if you're using hacking tools like kali linux and you're not doing anything to hide yourself it's kind of dangerous like you could get into trouble you need to learn learn learn hacking proxies and proxy chains that's how you hide yourself in this video i'm going to show you how they work and how to set them up in cali linux i also have a crazy cha... Read More
Key Insights
- Proxy servers are intermediaries that forward traffic to a target, causing the target to see the proxy server's IP address instead of the original public IP address. The presenter limits this technique to ethical hacking conducted with a business's explicit permission.
- A single proxy is not a guarantee of anonymity because the server may retain logs connecting incoming activity to the original user. If investigators contact that proxy provider, those records could reveal who sent the traffic through it.
- Proxy chaining routes traffic through multiple proxy servers before it reaches the target. This arrangement makes tracing the original source through server logs more difficult, but the presenter explicitly states that it is not foolproof and discovery remains possible.
- Dynamic chaining uses configured proxies in their listed order and skips a server when it is unavailable or unresponsive. The presenter prefers this mode because it can place several working proxies between the tester and the authorized target.
- Random chaining selects a proxy from the configured list instead of consistently following the full ordered chain. The transcript presents this behavior as useful for changing the IP address observed by a target across different connections.
- Proxy DNS prevents DNS requests from being sent directly from the tester's own address. Keeping the proxy_dns option enabled routes name-resolution activity through the proxy setup, avoiding the direct DNS request described as a possible source of exposure.
- Proxy entries require a proxy type, server IP address, and port, with optional username and password fields when authentication is required. The demonstrated configuration uses SOCKS4 and HTTP entries, while the presenter identifies SOCKS5 and HTTPS as more secure options.
- ProxyChains is invoked by placing the proxychains command before another command. The demonstrations launch Firefox and run Nmap TCP connect scans through configured proxies, then use a public IP search to confirm that the visible address matches the proxy route.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How do you configure ProxyChains on Kali Linux?
Locate proxychains.conf with the locate command, open the file with elevated privileges in an editor, and enable dynamic_chain by removing its leading comment marker. Add a comment marker to strict_chain, leave proxy_dns enabled, and comment out the default loopback proxy entry if Tor is not being used. Finally, add each proxy using its type, IP address, and port, then save the file.
Q: What is proxy chaining and how does it work?
Proxy chaining sends a connection through multiple proxy servers before it reaches the target. Each server passes the traffic to the next server in the configured route, and the target sees the final proxy's IP address rather than the tester's public address. The extra hops can make tracing the original source through multiple sets of logs more difficult, but they do not make identification impossible.
Q: What is the difference between dynamic and random chains?
Dynamic mode processes proxy servers in the order listed in the configuration and skips a server when it is unavailable, unresponsive, or otherwise unusable. Random mode chooses a proxy from the configured list, which can change the address observed by the target. The presenter chooses dynamic mode because it can route traffic through several configured proxies rather than selecting one proxy from the list.
Q: Why should proxy DNS remain enabled in ProxyChains?
Proxy DNS should remain enabled because a direct DNS request can reveal the address from which the tester is resolving a target's domain name. The transcript explains that disabling this setting allows the DNS request to originate from the tester instead of passing through the proxy. Keeping proxy_dns active makes name-resolution requests use the configured proxy route along with the other connection traffic.
Q: How do you add a proxy server to proxychains.conf?
Add a line containing the proxy type, the server's IP address, and its port, separated by spaces. If the proxy requires authentication, the configuration format also provides fields for a username and password. The demonstration adds one SOCKS4 proxy and later adds an HTTP proxy using port 8888, allowing dynamic mode to connect through both entries in their listed order.
Q: How can you verify that ProxyChains is working?
Prefix the Firefox command with proxychains and open a website through the resulting browser session. Review the terminal output to confirm that the DNS request and website connection passed through the configured proxy. Then search for the public IP address and compare the result with the proxy address. In the demonstration, the displayed address matches the proxy being used and indicates a location in Thailand.
Q: How do you run an Nmap scan through ProxyChains?
Place proxychains before the Nmap command so ProxyChains handles the connection route. The demonstration uses an Nmap TCP connect scan with the -sT option and checks ports 80 and 443 on an IP address. Terminal output shows the connection traveling through the configured proxy chain. Such scanning must be limited to ethical testing for which the tester has explicit permission.
Q: Does ProxyChains make a hacker completely anonymous?
No. The presenter explicitly says that proxy chaining is not foolproof and that no solution guarantees a person will never be discovered. A proxy server may store logs that connect the original user to later traffic, and investigators may request those records. Adding multiple proxies makes the tracing process more difficult, but it does not remove the need for authorization or eliminate the possibility of identification.
Summary & Key Takeaways
-
Proxy servers act as intermediaries between a tester and a target. Instead of receiving traffic directly from the tester's public IP address, the target sees the proxy server's address. A single proxy can still keep logs, so it should not be treated as a guaranteed method of remaining unidentified.
-
Proxy chaining routes connections through multiple proxy servers before reaching the target. In Kali Linux, ProxyChains can use dynamic or random behavior. Dynamic mode follows the configured order while skipping unavailable proxies, whereas random mode selects a proxy from the supplied list to vary the apparent source address.
-
ProxyChains is configured through proxychains.conf, which the presenter locates before editing. The setup enables dynamic_chain, disables strict_chain, retains proxy_dns, comments out the default loopback entry, and adds proxies by type, IP address, and port. Browser checks and TCP connect scans demonstrate whether the chain works.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from NetworkChuck 📚

Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator