How Does OpenClaw Work, and Is It Safe?
TL;DR
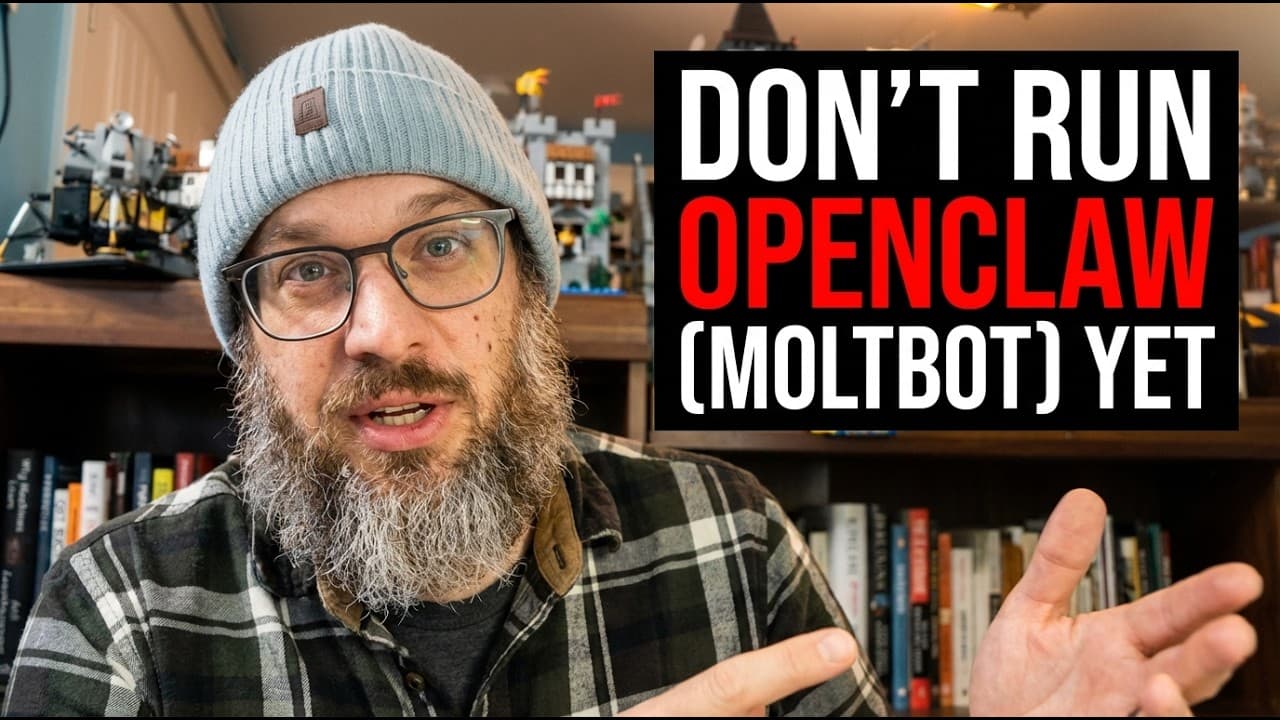
OpenClaw is a local-first AI agent that can read messages, access files, automate browsers, run shell commands, and complete tasks through familiar messaging apps. Its usefulness depends on broad permissions, but those same permissions create serious risks from exposed gateways, malicious skills, prompt injection, and credential theft, making careful deployment and security controls essential.
Transcript
In hundreds of cities across the globe right now, developers are queuing up to buy Mac minis specifically to give an AI agent root access to their digital life. And they are not alone. Apple's entire supply chain is feeling it. You can see literal spikes in Google Trends. Cloudflare's stock is up over 20% because this thing uses Cloudflare. What is... Read More
Key Insights
- OpenClaw is a local-first gateway service that connects messaging platforms such as WhatsApp, Telegram, Signal, and iMessage to an LLM backend, then uses skills to perform actions including browser automation, file access, shell commands, and calendar integration.
- Local-first operation keeps the gateway, conversation history, and credentials on the user’s machine, but it does not necessarily keep AI processing local. Queries still reach Anthropic or OpenAI when users select their APIs instead of an available local model such as Ollama.
- The project’s growth was exceptionally rapid, reaching 9,000 GitHub stars within 24 hours, 60,000 after a week, and more than 82,000 later. That popularity attracted developers, security researchers, market attention, impersonators, cryptocurrency speculators, and opportunistic scammers.
- The forced rebrand created an operational security failure because the old GitHub name and X handle were released before the replacements were secured. Scammers captured both during an approximately ten-second gap and used the project’s visibility to support impersonation and token promotion.
- A fake token on Solana reportedly reached a $16 million market capitalization before collapsing. Steinberger denied involvement and warned that any project listing him as a coin owner was a scam, illustrating how rapidly identity confusion can become financially consequential.
- The gateway’s former authentication logic trusted localhost connections by default, allowing reverse-proxy traffic to be mistakenly treated as local. Researchers found hundreds of exposed instances, including at least eight with unrestricted access to items such as API keys, bot tokens, conversations, and command execution.
- Prompt injection is a structural risk because OpenClaw reads incoming content and can act on it with substantial permissions. One researcher demonstrated that a malicious email could exploit an integrated instance and obtain a private key and control in under five minutes.
- Agent usefulness and agent security are in direct tension because meaningful automation requires access to files, credentials, communications, and commands. The broader an agent’s authority becomes, the larger its attack surface grows and the more damaging a successful manipulation or compromise can be.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What is OpenClaw and what can it do?
OpenClaw is a local-first AI assistant that runs a gateway service on the user’s hardware and communicates through existing messaging applications. It can connect to WhatsApp, Telegram, Signal, and iMessage, coordinate requests with an LLM, and use skills for email triage, response drafting, browser automation, form completion, file access, shell commands, calendars, flight searches, and morning briefings.
Q: How does OpenClaw work technically?
OpenClaw maintains websocket connections to supported messaging platforms and routes user requests through an LLM backend. Claude is commonly used, while GPT-4 and local models such as Ollama are also described as options. A library of skills supplies practical capabilities, including browser control, filesystem access, shell execution, and calendar integration, allowing the assistant to act instead of merely suggesting steps.
Q: Does OpenClaw keep all data on the local machine?
OpenClaw keeps its gateway, conversation history, and credentials on the user’s own machine under its local-first architecture. However, local-first does not mean that every operation remains local. When the agent uses Anthropic or OpenAI APIs, queries leave the machine for processing. Fully local processing requires using an available local model such as Ollama.
Q: Why did Clawdbot change its name to Moltbot and OpenClaw?
Anthropic’s legal team sent Peter Steinberger a trademark notice because the Clawdbot name was considered too close to Claude. The project was renamed Moltbot during its period of rapid growth and was subsequently renamed OpenClaw. Steinberger said the OpenClaw name would remain and that trademark searches for it had returned clear results.
Q: What happened during the ten-second account-name gap?
During the rebrand, Steinberger released the old GitHub name and X handle before securing the replacement identities. Crypto scammers who were monitoring the project captured both names within an approximately ten-second window. Fake accounts then multiplied, and a Solana token exploited the confusion, reportedly reaching a $16 million market capitalization before collapsing and harming late buyers.
Q: What security vulnerabilities were found in OpenClaw deployments?
Researchers found that the gateway formerly trusted localhost connections by default, which became dangerous when reverse proxies made outside traffic appear local. Hundreds of exposed instances were identified, and at least eight manually examined systems were completely open. Accessible data included API keys, Telegram bot tokens, private conversations, Signal configuration, credentials, and command-execution privileges. The localhost authentication issue was later fixed.
Q: How can prompt injection compromise an OpenClaw agent?
Prompt injection can occur when the agent reads an email or message containing malicious instructions and interprets those instructions as commands rather than untrusted content. Because the agent may access credentials, files, and shell commands, manipulation can cause serious damage. A researcher demonstrated a malicious email that obtained a private key and control from a vulnerable integrated instance in under five minutes.
Q: Why are third-party OpenClaw skills risky?
Third-party skills are risky because downloaded code is treated as trusted code, while the described marketplace had no moderation process. A researcher uploaded a harmless skill, artificially increased its displayed download count to 4,000, and watched developers in seven countries install it. The demonstration showed that a malicious publisher could potentially exploit apparent popularity to distribute dangerous code to unsuspecting users.
Summary & Key Takeaways
-
OpenClaw began as Peter Steinberger’s personal tool for managing digital tasks and rapidly became a viral open-source project. It runs a gateway on the user’s hardware, connects messaging platforms to an LLM, and uses skills for browser automation, file access, shell commands, calendars, email, and other practical actions.
-
The project’s forced rename from Clawdbot to Moltbot triggered a chaotic ten-second gap in which scammers captured released account names. A fake Solana token subsequently reached a reported $16 million market capitalization before collapsing, while impersonation accounts and false claims about Steinberger’s involvement spread across the project’s growing community.
-
Security researchers found exposed gateways, accessible credentials, an authentication bypass, prompt-injection risks, and an unmoderated skill marketplace. Although some vulnerabilities were patched, the central problem remains architectural: useful agents require access across boundaries that operating systems and security teams spent years creating to restrict software behavior and contain compromises.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from AI News & Strategy Daily | Nate B Jones 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator