How to do ethical hacking and red team testing
TL;DR
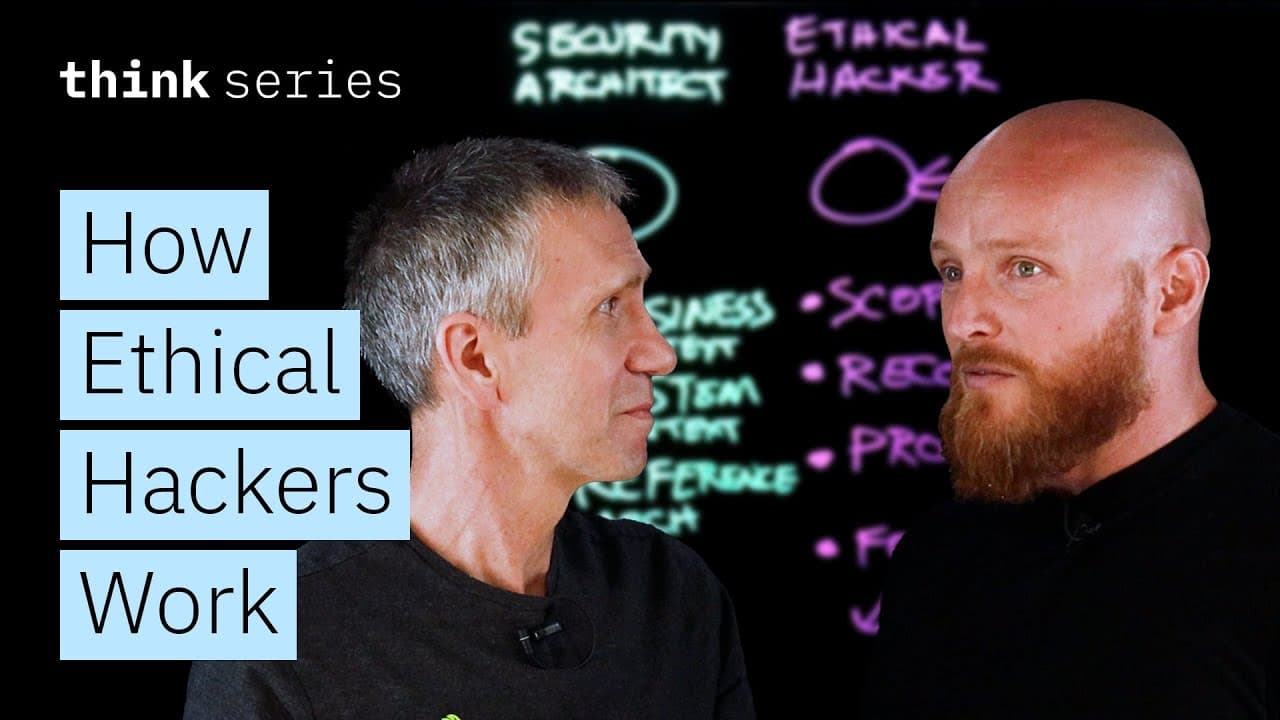
Ethical hacking is organized into vulnerability scanning, penetration testing, and adversarial simulation with clear goals and rules of engagement. Engagements are time bounded and deliverables focused on improving client security. A referee team and thorough reporting connect people, processes, and technology to defend against real threats.
Transcript
Welcome back to the second video in our series on ethical hacking. In the first video, we took a look at the role of the ethical hacker in general. In this video, we're going to do a little bit deeper dive into what the job involves, the actual tasks and considerations that an ethical hacker has to do. And in the final video, we'll take a look ... Read More
Key Insights
- Vulnerability scanning is the automated, big picture assessment used to identify potential weaknesses.
- Penetration testing involves a skilled tester exploiting vulnerabilities to understand impact and feasibility.
- Adversarial simulation, or red teaming, replicates a real world threat actor to test defense and response.
- Engagements must have defined goals and rules of engagement to guide testing activities.
- Time and budget constraints shape how testing is planned, conducted, and scoped.
- Reporting is a central deliverable, clarifying findings and recommended mitigations.
- Blue team involvement varies and may be unaware in some red team scenarios to test detection and response.
- People, processes, and technology must all be strengthened to actually improve security.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How to start an ethical hacking engagement and define goals
An ethical hacking engagement begins by defining two main buckets: goals and rules of engagement. Goals address what you want to learn, such as the ability to detect and prevent a bad actor, and the types of scenarios to test like financial theft or data exfiltration. Rules of engagement set boundaries, timelines, and safety constraints to ensure responsible testing.
Q: What is the difference between vulnerability scanning and penetration testing
Vulnerability scanning is the automated, broad sweep to identify vulnerabilities across a system, providing a big picture view. Penetration testing is more focused and hands on, with a skilled tester exploiting vulnerabilities to understand real world impact and exploit feasibility. Both are distinct steps in the testing ladder, with different time requirements and outcomes.
Q: What is red teaming and why is it important
Red teaming, or adversarial simulation, aims to replicate a real world threat actor to test the organization from the attacker perspective. This approach evaluates not only system security but also people and processes, including detection and response capabilities, providing a more realistic assessment of overall security posture.
Q: How long do different testing engagements typically last
Engagements vary by scope: vulnerability scanning might take days, penetration testing weeks, and red team exercises months. The time frame is determined by client needs, budget, and the level of realism desired, with longer engagements allowing deeper testing and more thorough reporting.
Q: What role does reporting play in an ethical hacking engagement
Reporting is essential, translating technical findings into actionable recommendations. It communicates what was discovered, how it was exploited, and what defenses are needed, serving as the primary deliverable that enables the client to improve security posture across people, processes, and technology.
Q: Who is the referee team in a red team test and what do they do
The referee team coordinates the exercise, communicates between red and blue teams, and ensures safety and scope are maintained. They manage information flow, control the testing pace, and help socialize findings, acting as the official regulators of the engagement to keep it effective and safe.
Q: What is the difference between ethical and unethical hacking
Ethical hacking operates under rules and within agreed constraints, with client consent and documented scope. It emphasizes safety, controlled testing, and reporting to improve defenses. Unethical hacking ignores boundaries, potentially causes harm, and aims to disrupt or steal without accountability or authorization.
Q: How do blue teams participate in red team engagements
Blue teams may be informed or unaware depending on the testing scenario. They are the defense side, tracking detection, response, and recovery. In some exercises they receive updates and status calls, while in others they are tested without prior knowledge to measure real time defenses and incident response effectiveness.
Summary & Key Takeaways
-
A high level of ethical hacking involves three main activity buckets, starting with vulnerability scanning and moving up to adversarial simulation, each with its own scope and purpose.
-
The process requires defined goals and rules of engagement, ensuring testing is safe, controlled, and aligned with client needs and constraints.
-
Deliverables and reporting are critical, translating technical findings into actionable recommendations that improve the client’s security posture across people, processes, and technology.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator