How did Carbanak hackers steal from banks?
TL;DR
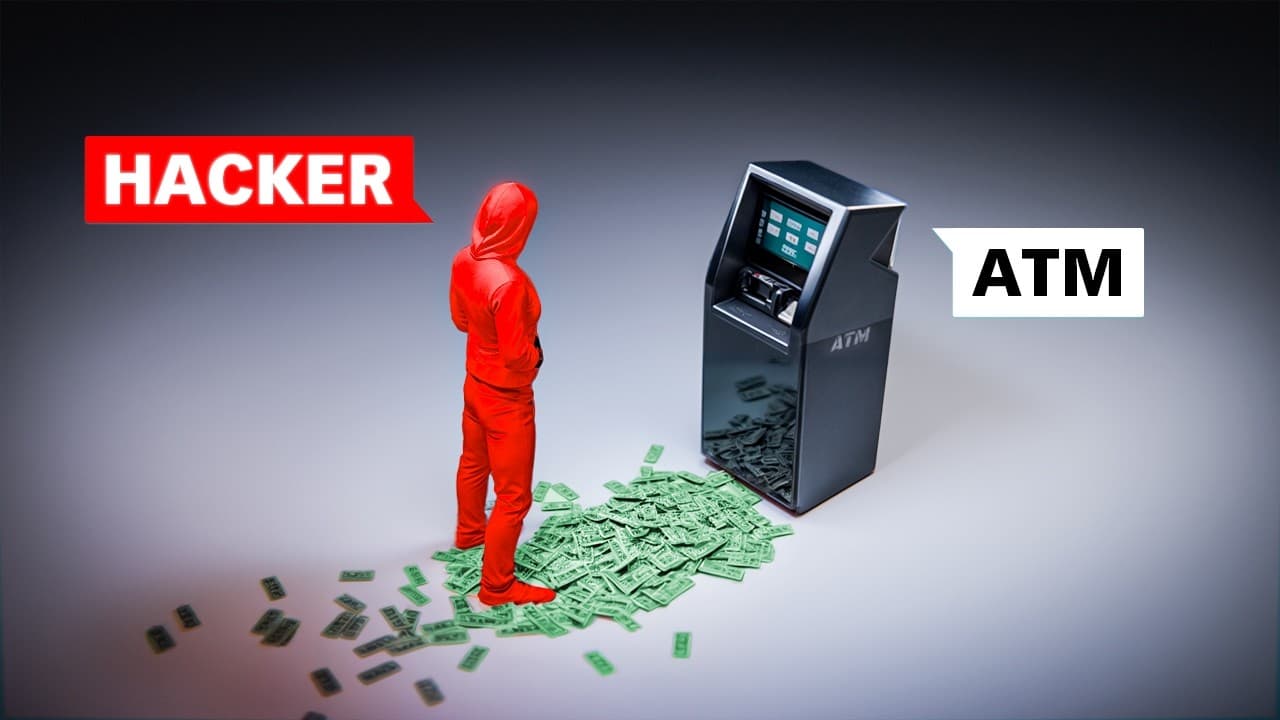
Carbanak attackers gained initial access through targeted email phishing and Word exploits to install back door malware. They then moved laterally, captured administrator credentials, and studied bank processes to quietly transfer funds or trigger ATM cashouts, enabling multi‑country thefts before being confronted by investigators in a global chase.
Transcript
July 10th 2016 two men are walking into the entrance of a bank in Taipei they're wearing medical masks and Fisher hats one of them guards the entrance while the other stands in front of the ATM he doesn't do anything though he doesn't withdraw money with a card nor does he try to blow it up he just Waits and then something curious happens the ATM s... Read More
Key Insights
- Carbanak gained initial access via phishing emails and Word exploits to deliver malware.
- The attackers moved laterally to reach the domain controller, giving them control over key servers and money transfer systems.
- Three transfer methods existed: manipulating balances, cashing out ATMs, and updating databases to falsely create large balances.
- The group observed bank processes for months before acting, ensuring precise timing for transfers.
- Money was moved through account manipulation and through ATMs using money mules and fake accounts.
- Investigators linked victims across many countries, tracing activity to the master mind and server infrastructure.
- The operation involved collaboration with Europol, FBI cyber teams, and other authorities to disrupt servers and seize funds.
- Recovery efforts recovered a large portion of the stolen money and led to sentencing of some mules and masterminds.
- More videos from this channel:
- More from this channel: fern
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: A real search query question about the video (e.g. 'How to...', 'What is...', 'Why does...', 'When should...'). Question 1
Carbanak was a highly coordinated cyber heist operation targeting banks and financial institutions across multiple countries. The attackers used spear phishing and Word document exploits to install back door malware, then pivoted to gain domain controller access which gave them control over money transfer systems. They studied the bank processes for months, identified how transfers were logged, and manipulated accounts to move funds or trigger ATM cashouts without immediate detection. The case illustrates how cyber criminals combine phishing, malware, credential theft, and careful timing to commit large scale financial theft.
Q: Question 2
The attackers established an initial foothold by sending emails with Word attachments that exploited vulnerabilities, allowing malware installation. Once inside, they deployed back doors and keyloggers to capture credentials and observe transaction workflows. This multi stage access enabled them to map vulnerabilities in security controls, anticipate human and system responses, and plan a sequence of transfers that would minimize suspicion while maximizing stolen sums.
Q: Question 3
A crucial step in the operation was gaining control of the bank domain controller, which functions as the heart of a Windows based network. With control over the domain controller, the hackers could impersonate legitimate administrators, modify transaction logs, and orchestrate transfers or ATM cashouts across the network. This level of access made it possible to alter balances or release cash without triggering standard checks for hours.
Q: Question 4
The group employed at least three distinct methods to move money, including transferring funds to their own accounts, manipulating ATM withdrawals, and updating databases to reflect fictional balances. By restructuring balances rather than creating new ones, they could exploit bank check intervals and withdraw large sums with minimal immediate scrutiny, illustrating sophisticated financial manipulation.
Q: Question 5
Money mules and coordinated cashouts were a key component of the operation. The attackers used money mules to collect cash from ATMs and then transfer or ship it to the organizers. They also used controlled debit card accounts with small balances to cause a large nominal transfer, causing the system to authorize large withdrawals without alerting standard monitoring thresholds.
Q: Question 6
Investigators globally linked victims and traced activity to the master mind through server infrastructure and the methods used. The operation spanned many banks and countries, prompting collaboration among Europol, FBI cyber teams, banks, and law enforcement. This collaboration helped disrupt command and control servers and led to asset recovery and prosecutions of several participants, demonstrating the power of international cooperation in cybercrime cases.
Q: Question 7
The timeline shows the attackers exploiting patience and surveillance, waiting months before taking action to avoid suspicion. They leveraged the knowledge gained from monitoring employees and transaction flows to choose opportune moments for transfers and ATM cashouts. This patient, methodical approach is emblematic of high level cyber heists where timing and stealth trump speed.
Q: Question 8
The case underlines the complexity of modern cyber crimes where criminals blend malware, social engineering, credential theft, and financial manipulation. It demonstrates the need for layered security, robust monitoring of domain controllers, timely software updates, and international information sharing to detect, disrupt, and recover from large scale financial cyber attacks.
Summary & Key Takeaways
-
A detailed account of the Carbanak operation showing how phishing, malware, and credential theft allowed long term access to bank networks and payment systems, enabling massive unauthorized transfers and ATM cashouts across multiple countries while investigators linked the pattern to a coordinated transnational group.
-
The narrative follows the hackers from initial intrusion through to the eventual identification of the master mind, highlighting the use of domain controller access and cunning manipulation of transaction records to evade early detection for months.
-
The documentary underscores how multinational collaboration among banks and law enforcement helped map the attackers' methods and recover a significant portion of stolen funds, illustrating a high profile case of cyber heists on a global scale.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from fern 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator