How Does Agentic Runtime Security Protect Non-Human Identities?
TL;DR
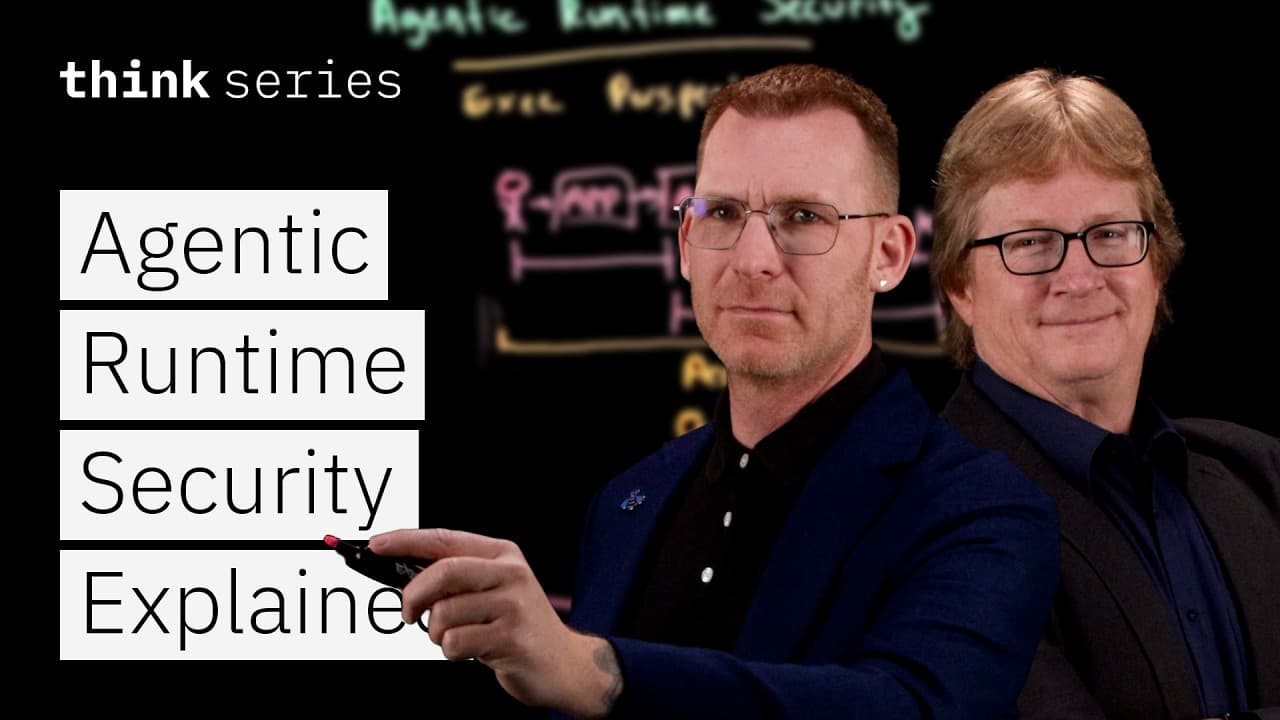
Runtime identity protection secures AI agents by assigning each instance a unique identity, stripping standing privileges, granting session-level access only when needed, and checking authorization when an agent connects to sensitive resources. With an estimated 45 to 90 non-human identities for every human identity, organizations also need intent-based delegation and audit logging. Read on for the five imperatives of agentic runtime security.
Transcript
Hey everybody, we're here to talk today about probably the most white hot topic in IT today. And that is agentic AI, in particular, how you actually deploy agentic AI with agentic runtime security. This topic begins and ends really with identity and access management. And the reason that's causing a lot of problems right now. Is because when you ta... Read More
Key Insights
- Agentic AI is a non-human identity because an agent is a software workload, such as TypeScript or Python code, running on infrastructure including containers, Lambda, or virtual machines and receiving an identity to access other systems.
- Non-human identities are estimated in the discussion to outnumber human identities by roughly 45 to 90 for every human identity, greatly expanding the identity-related surface that organizations must register, govern, observe, and audit.
- Traditional human-centered identity management often protects only the connection from a user or application to the first agent. Embedded agents can continue toward databases, mainframes, and other sensitive resources without equivalent controls across the full chain.
- Accountability requires a unique identifier for every agent instance so its behavior can be traced precisely. If an agent inherits and impersonates a user's identity, security records cannot reliably distinguish the agent's actions from the user's actions.
- Least privilege for agents requires stripping standing permissions and issuing dynamic privileges only for the necessary request, action, and session. An HR agent, for example, should not retain continuous authority to onboard or off-board employees.
- Secure delegation ties a user's request, the selected agent, and the intended action into one auditable workflow. This connection becomes especially important when agents perform banking transactions, transfer funds, or provision infrastructure in cloud and on-premises environments.
- Last-hop enforcement checks each external connection near real time at the point of use. Authorization granted when an agent was deployed one or two months earlier is insufficient for deciding whether a specific action is permitted in the current session.
- Agentic runtime security depends on orchestration, governance, and observability working together. These capabilities direct identity flows, apply policies, provide proof of control, expose posture and threats, and give security, IT, and development teams a shared view of risk.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How does runtime identity protection secure AI agents?
Runtime identity protection registers each AI agent and gives every instance a unique identifier. It strips standing privileges, grants dynamic access for a specific request and session, records delegated intent, and checks authorization when the agent connects to a sensitive resource.
Q: Why are AI agents considered non-human identities?
AI agents are software workloads written in technologies such as TypeScript or Python. They run on infrastructure such as containers, Lambda, or virtual machines and receive identities that let them access other systems.
Q: Why do traditional identity and access controls leave AI agents exposed?
Traditional human-centered identity and access management often protects the path only from the user or application to the first agent. Protection can break down when embedded agents call other agents, databases, mainframes, or other back-end resources.
Q: Why does every AI agent instance need a unique identity?
A unique identifier makes each agent instance accountable and allows its actions to be traced. If an agent inherits the invoking user's identity, security records cannot distinguish the agent's actions from the user's actions.
Q: How should least privilege work for an AI agent?
All standing privileges should be stripped from the agent. Dynamic privileges should then be granted only for the required request, action, and session, so an HR agent does not continuously retain authority to onboard or off-board employees.
Q: How can organizations secure delegated actions by AI agents?
Delegation should connect the requesting user, the selected agent, and the intended action. The workflow should preserve the user's intent and include audit logging so organizations can determine who authorized and performed an action.
Q: What is the last-mile security problem for AI agents?
The last-mile problem occurs when an agent reaches a sensitive resource without a current authorization check. Standing privileges or shared database credentials make access difficult to evaluate and revoke, especially when agents act at machine speed.
Q: What are the five imperatives for agentic runtime security?
The five imperatives begin with registering agents and stripping their standing privileges. They also require tying actions to user intent, enforcing policy at the point of use, and producing proof of control through an end-to-end audit record.
Summary & Key Takeaways
-
Agentic AI creates an identity and access management challenge because agents are non-human identities that can call other agents and sensitive back-end resources. Human-centered controls often protect only the path from a user to the first agent, leaving embedded agents and subsequent resource connections without sufficient accountability, authorization checks, or auditability.
-
The proposed security model registers every agent, removes standing privileges, grants dynamic access at the session level, ties delegated actions to the requesting user's intent, and enforces policy at the point of use. These controls address overprivilege, impersonation, unclear delegation, shared credentials, and unverified last-hop access to sensitive systems.
-
Secure deployment depends on orchestration, governance, and observability working across human and non-human identities. Orchestration directs identities and actions, governance applies policies and supports proof of control, while observability exposes security posture and threats. Security, IT, and development teams must use this visibility to coordinate risk management throughout the agent lifecycle.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator