How Does AI Accelerate the Quantum Encryption Threat?
TL;DR
AI-assisted research reportedly reduced estimates for the quantum resources needed to attack widely used encryption, prompting Google and Cloudflare to target 2029 for post-quantum migration. No cryptographically relevant quantum computer exists today, but organizations should audit vendors, protect data vulnerable to harvest-now-decrypt-later attacks, and prepare to replace both encryption and authentication systems.
Transcript
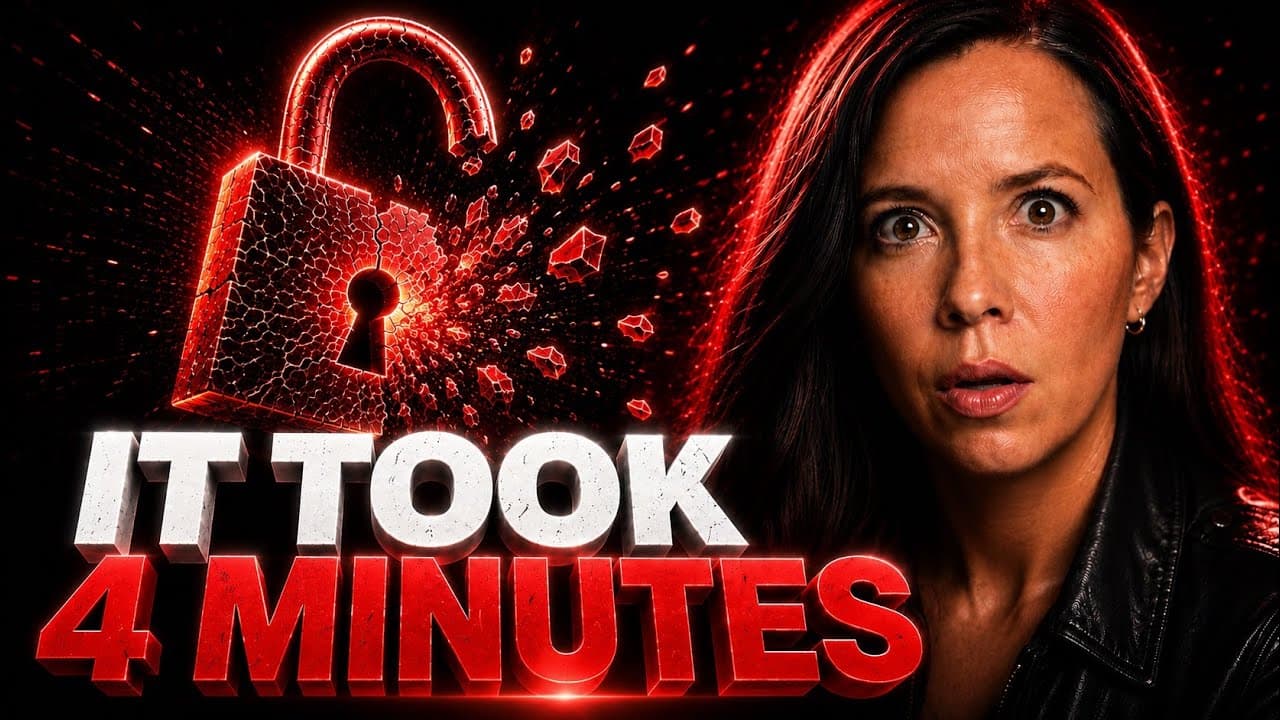
In 2024, experts thought breaking the encryption that protects the internet would take a quantum computer with around 20 million cubits. As of this spring, that number dropped to under 500,000. And the thing that pulled it down that fast wasn't a bigger machine. It was AI. Let me say that again because I want it to land. The estimate of what it tak... Read More
Key Insights
- Q-Day is the point when a quantum computer becomes powerful enough to break cryptography used for bank logins, messages, browser connections, Bitcoin, other cryptocurrency wallets, and much of the public web.
- AI is described as the reason projected attack costs fell, because it helped researchers redesign and translate quantum attack algorithms rather than directly creating a larger or more powerful quantum computer.
- Google's Quantum AI team reported a roughly twentyfold reduction in the resources estimated to attack ECDSA-256, with the breakthrough verified through a zero-knowledge proof that avoided publicly revealing the attack recipe.
- Oratomic research suggested that RSA-2048 could be attacked with as few as 10,000 reconfigurable atomic qubits, and its authors said AI was instrumental in developing the required algorithm translation.
- A cryptographically relevant quantum computer does not exist today, and neither RSA nor Bitcoin has been broken, so the resource counts and projected timelines remain estimates rather than demonstrated attacks.
- Harvest-now-decrypt-later attacks create present-day risk because well-funded adversaries can record encrypted messages, financial records, and company secrets now, then decrypt the stored archive when capable quantum hardware becomes available.
- Authentication is a broader challenge than data secrecy because quantum attacks could enable forged software updates, code-signing certificates, API credentials, and trusted-system identities across legacy products, external vendors, and unmanaged devices.
- Post-quantum preparation starts with asking software vendors for their migration timelines, identifying long-lived sensitive information, and building expertise that connects current cryptography with quantum-resistant systems before announced retirement deadlines arrive.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What is Q-Day and what could it put at risk?
Q-Day is the projected point when a quantum computer becomes powerful enough to defeat encryption used across the modern internet. The transcript identifies bank logins, private messages, browser connections, Bitcoin, other cryptocurrency wallets, and public-web infrastructure as potentially exposed. It also emphasizes that Q-Day would not instantly break every system, because deployment conditions and individual systems would differ.
Q: How did AI reduce the estimated resources for quantum attacks?
AI reportedly helped researchers redesign or translate the algorithms used in quantum attacks, lowering the projected hardware requirements without anyone first building a giant new machine. Google's Quantum AI result showed a roughly twentyfold reduction for attacking ECDSA-256. Oratomic's authors separately said AI was instrumental in developing an algorithm translation for a proposed RSA-2048 attack on neutral-atom quantum machines.
Q: Has a quantum computer already broken RSA or Bitcoin?
No. According to the transcript, nobody has broken RSA or Bitcoin, and a cryptographically relevant quantum computer does not currently exist. The cited qubit requirements come from research estimates, which may prove inaccurate in either direction. The immediate concern is that improved attack designs have reduced projected resource needs and may shorten the time available for migration.
Q: Why are Google and Cloudflare using 2029 as a deadline?
Google moved its internal post-quantum migration target to 2029, and Cloudflare accelerated its own deadline to the same year after the reported research results. IBM's Quantum Safe team also lists attacks as a realistic possibility as early as 2029, while NIST set 2030 for starting RSA retirement. The transcript presents this alignment as a growing consensus about urgency.
Q: What does harvest now, decrypt later mean?
Harvest now, decrypt later is a strategy in which a patient, well-funded adversary records encrypted information today and stores it until a capable quantum computer becomes available. The adversary could then decrypt the accumulated messages, financial records, or corporate secrets. Consequently, information that must remain confidential through 2029 may already face exposure even though current encryption has not been broken.
Q: Why is authentication harder to migrate than encryption?
Encryption primarily conceals information, while authentication establishes whether a person, device, update, or service is genuinely trusted. The transcript warns that a quantum-capable attacker might forge software updates, code-signing certificates, API credentials, or trusted-system identities. Replacing these mechanisms is harder because they are embedded across legacy systems, vendor products, and devices that an organization may not directly control.
Q: How should a business prepare for post-quantum security?
A business should begin by asking each software vendor for a specific post-quantum migration timeline. Missing or vague answers help reveal which parts of the technology stack may be least prepared. The business should also identify information requiring long-term secrecy and review authentication dependencies, including software updates, API keys, certificates, legacy systems, vendor services, and externally controlled devices.
Q: What skills could become valuable during post-quantum migration?
The transcript argues that people who can connect today's cryptographic infrastructure to quantum-resistant replacements could gain negotiating leverage over the next decade. Valuable work includes understanding existing encryption and authentication dependencies, evaluating vendor readiness, and planning migrations around announced institutional deadlines. The opportunity is tied to practical implementation because organizations must update interconnected systems rather than merely understand quantum computing conceptually.
Summary & Key Takeaways
-
AI changed the projected quantum threat by helping researchers redesign attacks rather than by producing a larger quantum computer. The transcript cites Google's roughly twentyfold resource reduction for attacking ECDSA-256 and separate Oratomic research suggesting that RSA-2048 could be attacked using as few as 10,000 reconfigurable atomic qubits.
-
Google and Cloudflare selected 2029 as a post-quantum migration deadline, while NIST set 2030 for beginning the retirement of RSA. These dates do not prove that Q-Day will arrive on schedule, but the alignment among major organizations indicates that preparations for quantum-capable attacks are becoming more urgent.
-
Organizations face immediate exposure through harvest-now-decrypt-later collection, where adversaries store encrypted information for future decryption. The recommended response is to audit vendors, develop post-quantum migration skills, and address authentication infrastructure such as code-signing certificates, API keys, and software-update mechanisms, not merely systems that conceal stored or transmitted data.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from Julia McCoy 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator