How to Scan Networks for Vulnerabilities with Nmap
TL;DR
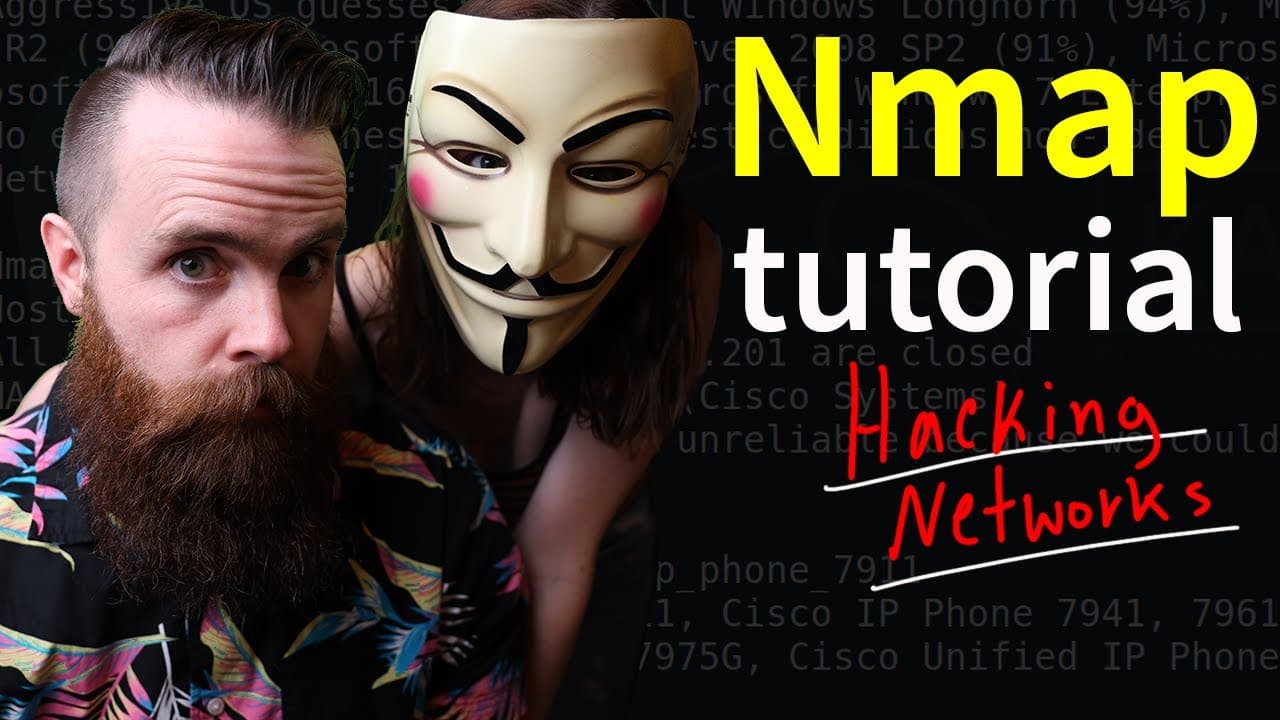
Use Nmap to discover active hosts, identify open ports, detect operating systems, and enumerate service versions across an authorized network. Start with host discovery, use targeted TCP connect or SYN scans for ports, then apply OS detection or aggressive scanning when deeper enumeration is needed, while recognizing that intrusion detection systems and modern firewalls may notice scanning activity.
Transcript
with just one command I scanned my entire network now my hacking targets found out what operating systems are running what ports are open and even found vulnerabilities that I can exploit that is the power of in map a free essential tool for hackers and pretty much anyone and IT let's get started you need to learn learn learn hacking in a map or ne... Read More
Key Insights
- Nmap is a free network mapper that runs on Windows, macOS, and Linux. It can discover live hosts and enumerate information about selected targets, making it useful for examining devices and services across an authorized network.
- Host discovery is faster than manually pinging every possible endpoint. Using the shown discovery command against a 10.7.1.0/24 network found 15 active hosts in 2.71 seconds, while the network could contain 254 endpoints.
- Open ports indicate which services may be reachable on a host. Scanning ports 80 and 443 can help identify possible web servers because the tutorial associates those ports with website access, although an open result alone does not prove the system's purpose.
- A TCP connect scan completes the three-way handshake. Nmap sends a SYN packet, receives SYN-ACK when the target is listening, and sends ACK to establish the connection before resetting the short-lived conversation used to test the port.
- A SYN scan stops before completing a normal TCP connection. After receiving SYN-ACK from an open port, Nmap sends a reset instead of the final acknowledgment, creating what the tutorial calls a stealth or half-open scan.
- Stealth scanning is not guaranteed to remain undetected. Avoiding a completed connection may reduce some detection, but the tutorial warns that intrusion detection systems and modern firewalls can still recognize scanning behavior.
- Nmap scans the top 1,000 popular ports by default when no port is specified. In the demonstrated single-host TCP connect scan, that default operation completed in 0.17 seconds and returned results without requiring an explicit port list.
- Aggressive scanning combines several enumeration functions. The -A option performs operating-system detection, service-version checks, script scanning, and traceroute, producing detailed findings such as SSH host keys, Apache information, file-sharing details, and network distance.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How do you discover active hosts on a network with Nmap?
Run an Nmap host-discovery scan against the network range you are authorized to examine. The tutorial uses 10.7.1.0/24, a network that could contain 254 endpoints, and reports 15 active hosts in 2.71 seconds. This automates the process of checking which systems respond and avoids manually issuing a separate ping for every possible address.
Q: How do you scan ports 80 and 443 across a network?
Use Nmap with a TCP scan type, specify ports 80 and 443 with the port option, and provide the authorized network range as the target. The tutorial scans 10.7.1.0/24 and compares the results for each host. Open ports suggest that website-related services may be reachable, while closed ports make that role less likely.
Q: What is the difference between a TCP connect scan and a SYN scan?
A TCP connect scan completes the three-way handshake by sending SYN, receiving SYN-ACK, and replying with ACK. A SYN scan sends SYN and evaluates the response but does not complete the connection. After a SYN-ACK indicates an open port, it resets the exchange, which is why the tutorial describes it as half-open or stealthy.
Q: How does Nmap determine whether a TCP port is open?
Nmap tests the target port using TCP handshake behavior. It sends a SYN packet to request communication. If a service is listening, the host can reply with SYN-ACK, showing that the port is available. A connect scan then sends ACK, while the demonstrated SYN scan sends a reset and ends the exchange without establishing a full connection.
Q: Can a stealth Nmap scan avoid intrusion detection systems?
A SYN scan may be less intrusive because it does not complete the TCP three-way handshake, but the tutorial does not present it as invisible. Intrusion detection systems, including capabilities built into firewalls, may notice scanning activity. Modern security controls can also detect half-open behavior, so the stealth label should not be treated as a guarantee.
Q: What happens when no port is specified in an Nmap scan?
Nmap automatically checks the top 1,000 most popular ports when the command does not include a specific port. The demonstrated TCP connect scan targets one host and completes in 0.17 seconds. This default provides a broad initial view of commonly used ports without requiring the operator to list every port individually.
Q: How do you detect a target operating system with Nmap?
Use Nmap's capital O option against an authorized host. The tutorial explains that Nmap first determines whether the host is active, checks port behavior, and then makes its best operating-system estimate. The demonstrations identify one target as Linux and recognize another system as Windows Server 2012 R2, while also listing ports associated with the server.
Q: What information does Nmap aggressive scanning provide?
The capital A option combines operating-system detection, protocol or service-version checking, script scanning, and traceroute. In the examples, it reports an SSH host key, an SSH version, Apache on port 80, Red Hat Linux information, file-sharing details, and the route to the target. The deeper scan takes 128 seconds in one demonstration.
Summary & Key Takeaways
-
Nmap automates network discovery and enumeration across Windows, macOS, and Linux. A host-discovery scan found 15 active devices on a network that could contain 254 endpoints. This provides a faster alternative to pinging every address individually and establishes which systems are available for further authorized investigation.
-
Port scanning reveals which network services may be reachable. The tutorial checks ports 80 and 443 across a network, explains TCP connect and SYN scanning through the three-way handshake, and uses Wireshark captures to show SYN, SYN-ACK, ACK, and RST packets produced during different scan types.
-
Nmap can perform deeper enumeration through operating-system detection and aggressive scanning. The examples identify a Linux machine, recognize Windows Server 2012 R2, report SSH and Apache versions, expose file-sharing information, and produce a traceroute. The manual page provides additional switches for tailoring scans to specific objectives.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from NetworkChuck 📚


Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator