How to choose RBAC or ABAC for access control
TL;DR
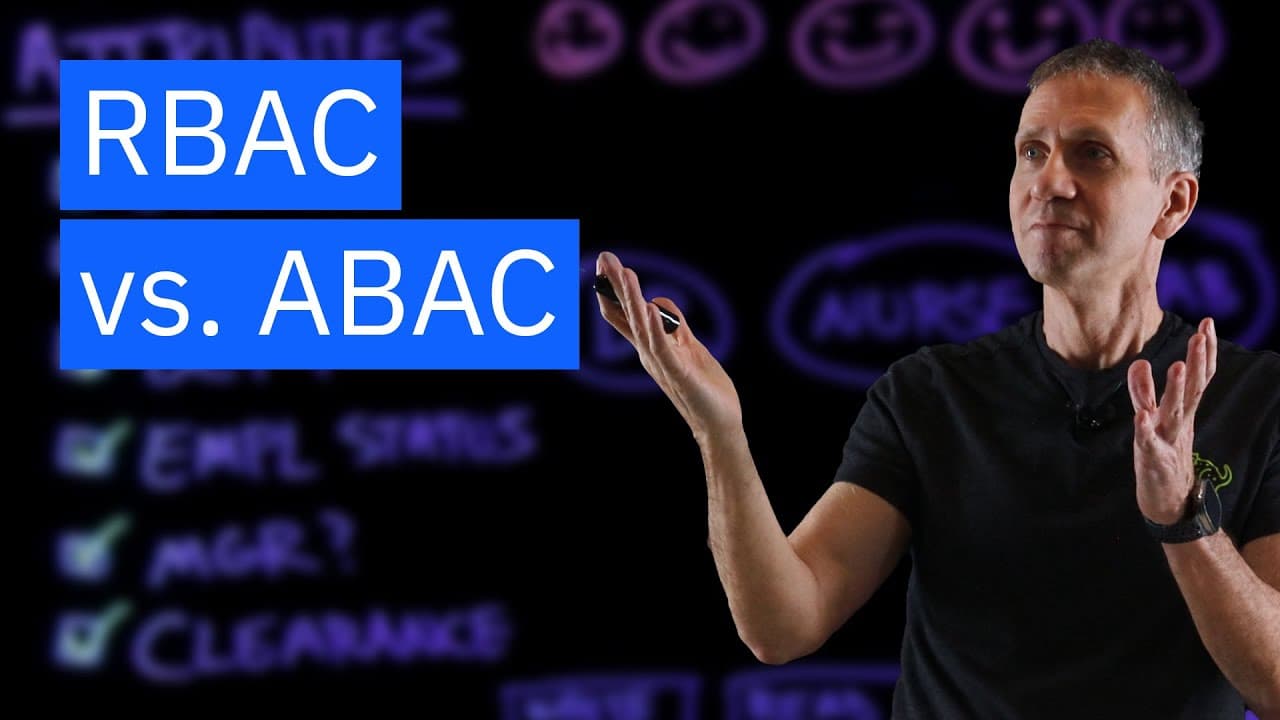
RBAC and ABAC offer different ways to decide access. RBAC groups users by roles and grants permissions accordingly, while ABAC uses attributes like geography, department, and clearance to decide access. A hybrid approach can combine both to fit an organization’s structure and flexibility needs.
Transcript
Two questions for you: "who are you?" and "what are you allowed to do?" These are two questions that go into what we call "access control". Access control is involved in these two steps. I've talked a lot about this one in previous videos about authentication. This is where we get things like multi-factor authentication, password strength rules, pa... Read More
Key Insights
- RBAC simplifies access management by mapping individual users to roles.
- RBAC uses aggregated permission sets per role, reducing policy maintenance.
- ABAC defines access using attributes such as geography, position, department, employment status, and clearance.
- ABAC enables fine grained, context sensitive access decisions beyond roles.
- Hybrid approaches can combine RBAC and ABAC to leverage strengths of both models.
- Policy enforcement points mediate access requests, while policy decision points evaluate whether to grant access.
- RBAC is often preferred in hierarchical organizations for ease of control.
- ABAC is favored in dynamic environments where roles alone are insufficient.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How does RBAC simplify access control in large organizations?
RBAC simplifies access control by assigning users to roles such as doctor, nurse, or lab technician and then granting permissions based on those roles. This abstraction removes the need to manage individual access rights for every user, making it easier to scale as the organization grows. If new capabilities are added, they can be assigned to the relevant role rather than to each user.
Q: What is ABAC and what kinds of attributes does it consider?
ABAC is a method of access control that uses attributes to determine permissions. It considers attributes such as geography, position, department, employment status, whether someone is a manager, and their security clearance. Access is granted when a set of attribute based conditions are all true, enabling fine grained control that reflects real world scenarios.
Q: Can RBAC and ABAC be used together, and if so, how?
Yes, RBAC and ABAC can be used together in a hybrid approach. You can use RBAC to provide a high level, easy to manage framework by assigning users to roles and then apply ABAC rules on top of those roles to handle more dynamic or context dependent permissions. This allows both structure and flexibility in access control.
Q: What is the role of a policy enforcement point in access control architecture?
The policy enforcement point acts as the mediator that receives access requests and makes a decision based on the policy it is given. It queries the policy decision point to determine whether access should be granted. If approved, access is allowed; if not, access is blocked. The PEP is the enforcement layer in the model.
Q: What is the role of a policy decision point in access control architecture?
The policy decision point is the central decision making component that evaluates access requests against the defined policies and attributes. It returns a yes or no decision to the policy enforcement point. The PDP handles the hard work of interpreting policies, while the PEP enforces the resulting decision.
Q: Why might ABAC be preferred in a non hierarchical organization?
In non hierarchical organizations, ABAC offers greater flexibility by evaluating multiple attributes rather than relying on a fixed role structure. This allows access to be granted based on current context such as department, location, and clearance, enabling more precise and adaptive permissions than rigid role based models.
Q: What are the potential benefits of a hybrid RBAC and ABAC approach?
A hybrid approach can provide the simplicity of RBAC for high level access control while using ABAC to handle nuanced, context sensitive scenarios. This can improve scalability, maintain policy clarity, and allow dynamic adjustments without changing core role assignments. It also enables combining governance with operational agility.
Q: What does the video suggest about handling new capabilities in an RBAC world?
The video suggests that with RBAC you can add new capabilities by extending the relevant role rather than reworking individual user permissions. This keeps changes centralized and scalable, since new functions can be exposed to entire roles, and new employees can simply be mapped to existing roles to inherit the appropriate access.
Summary & Key Takeaways
-
RBAC simplifies access by mapping users to roles, then assigning permissions at the role level, reducing complexity as the organization grows.
-
ABAC uses flexible attributes to make fine grained access decisions, enabling dynamic policies that reflect real world conditions and user characteristics.
-
A hybrid RBAC and ABAC approach can leverage high level role definitions with attribute based rules to balance simplicity and flexibility across diverse environments.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator