How Does Google Secure Its Data Centers in 6 Layers?
TL;DR
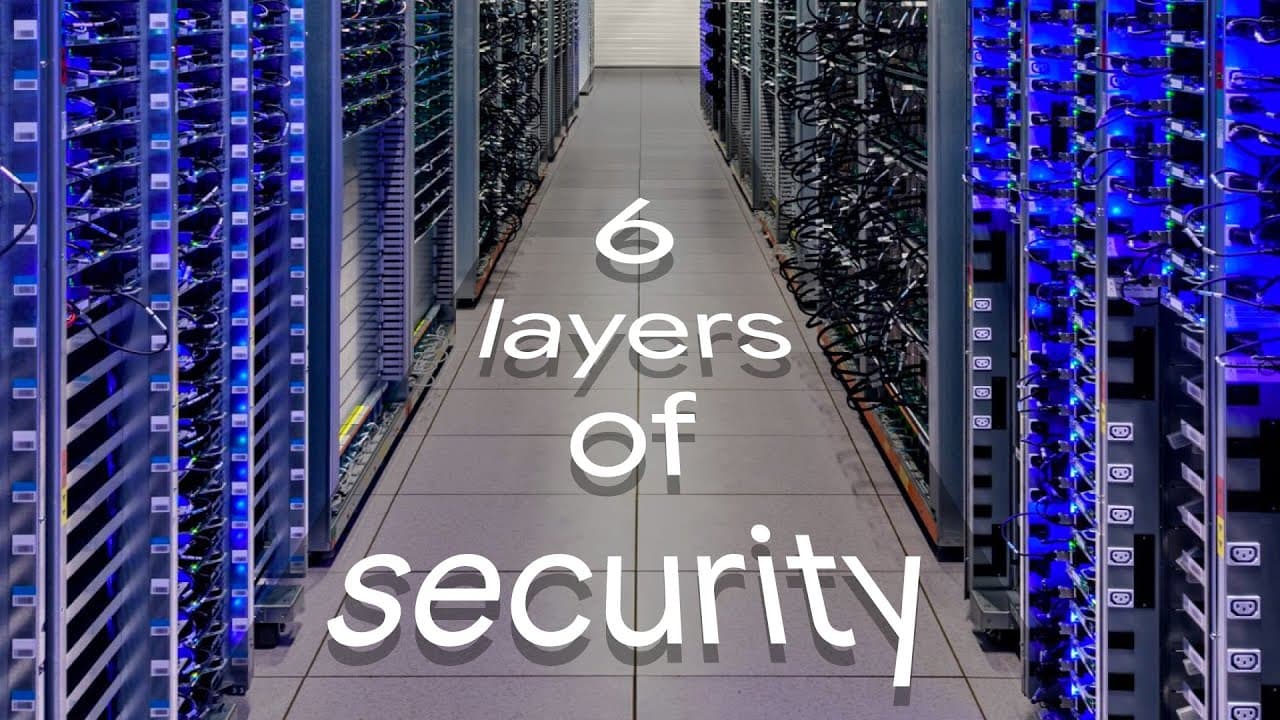
Google protects customer data at a typical data center with six layers of physical security: property boundaries, a secure perimeter, building access, a security operations center, the data center floor, and a disk erasure and destruction room. Access narrows at each layer, data at rest is encrypted, and two testing programs probe security from both outside and inside.
Transcript
[upbeat music] Wong: Hi, I'm Stephanie Wong, and I work for Google Cloud. While I could talk all day about cloud security, physical security at a Google data center is still pretty new to me, so today I'm on a mission to learn all about it by taking an inside look at the systems in place that protect customer data at a typical Google data center. L... Read More
Key Insights
- Layer one of Google data center security is the property boundary, which includes signage and fencing. It marks the outer edge of the site, and protection becomes stricter at each of the next five layers.
- The secure perimeter, layer two, combines smart fencing, overlapping cameras, 24/7 guard patrols, and a vehicle crash barrier. The crash barrier is designed to stop a fully loaded truck from driving through the front entrance.
- The perimeter fence is an anti-climb fence equipped with fiber. This technology alerts security when someone is near the fence or touches it, and thermal and standard cameras give clear footage at night as well as during the day.
- Building access, layer three, pairs ID badges with iris scans. The iris scan confirms the person holding the badge is the real owner, so a lost card cannot be used by someone else, and only one person may badge through a secure door at a time.
- The security operations center, layer four, monitors the data center 24/7, 365 days a year. Doors, cameras, badge readers, and iris scanners all connect to it, making it the brains of the security system that spots anything out of the ordinary.
- The data center floor, layer five, is visited by less than 1% of Googlers. Access is strictly as-needed, limited to technicians and engineers who must maintain, upgrade, or repair equipment, and data at rest is encrypted with customers able to hold their own keys.
- Layer six is the room where retired disks are erased or destroyed, and the fewest people may enter it. Drives arrive through a secure two-way locker system, and only technicians assigned to the room can take them out to process them.
- Google Cloud runs two security testing programs beyond the six layers. One hires outside companies to try to break into data center sites, while the other tasks Googlers with breaking security protocols from inside, and everyone passes full metal detection when leaving the floor.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What are the six layers of security at a Google data center?
A typical Google data center has six layers of physical security. Layer one is the property boundary with signage and fencing. Layer two is the secure perimeter with the main gate, smart fencing, cameras, and guards. Layer three is building access with badges and iris scans. Layer four is the security operations center. Layer five is the data center floor, and layer six is the disk erasure and destruction room.
Q: How does Google protect the perimeter of its data centers?
The secure perimeter, layer two, uses smart fencing, overlapping cameras, 24/7 guard patrols, and a vehicle crash barrier built to stop a fully loaded truck. The anti-climb fence carries fiber that detects when someone is near it or touches it. Thermal and standard cameras show night footage as clearly as daytime footage, and visitors are tracked from arrival so their movements can be correlated.
Q: Why do Google data centers use iris scans in addition to ID badges?
An ID badge alone proves only that someone holds the card, not that they are its owner. If a person lost their badge, someone else could try to use it. The iris scan at the secure lobby authenticates the person together with their ID, confirming the right individual has arrived. Secure areas also allow only one person to badge through a door at a time.
Q: What does the security operations center do at a Google data center?
The security operations center, or SOC, is layer four and monitors the data center 24/7, 365 days a year. Every door, camera, badge reader, and iris scanner connects to it, which makes it the brains of the security system. Its staff must detect anything out of the ordinary happening across the site and respond to it as it happens.
Q: Who is allowed on the Google data center floor?
The data center floor is layer five, and less than 1% of Googlers ever set foot there. Access is strictly as-needed: only technicians and engineers who must maintain, upgrade, or repair equipment are allowed in. Even these staff have access to the devices rather than readable data, because data at rest is encrypted and customers can issue and keep their own encryption keys.
Q: Can Google employees access customer data stored in data centers?
Google staff working on the data center floor can access the physical devices, but data at rest is encrypted. Customers can also issue and keep their own encryption keys. Google says it does this because protecting the privacy and security of its users' data is its highest priority, so physical access to hardware does not mean access to readable customer data.
Q: How does Google destroy old hard drives from its data centers?
Retired drives leave the data center floor through a secure two-way locker system into layer six, the room with the fewest permitted people. Only technicians assigned to that room can take drives from the locker. Each drive is scanned, and software decides whether it should be erased or destroyed. Drives marked for destruction go into a crusher that physically destroys the disk.
Q: How does Google test the security of its data centers?
Google Cloud runs two security testing programs on top of its six physical layers. One hires outside companies to try to break into data center sites from the outside. The other tasks Googlers with trying to break security protocols from the inside. Leaving is also strictly controlled: everyone passes full metal detection each time they exit the data center floor.
Summary & Key Takeaways
-
Google data centers use six layers of physical security. The first is the property boundary with signage and fencing. The second is the secure perimeter, with a main entrance gate, anti-climb fiber-equipped fencing, thermal and standard cameras, guards in vehicles and on foot, and a crash barrier that can stop a fully loaded truck.
-
Layer three controls building access with ID badges plus iris scans, so a lost card cannot be used by someone else, and only one person may badge through a secure door at a time. Layer four is the security operations center, which links doors, cameras, badge readers, and iris scanners and watches the site around the clock.
-
Less than 1% of Googlers ever enter the data center floor, layer five, which only technicians who maintain, upgrade, or repair equipment may access. Data at rest is encrypted and customers can keep their own keys. Layer six erases or crushes retired disks, and two testing programs probe security from outside and inside.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from Google Cloud Tech 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator