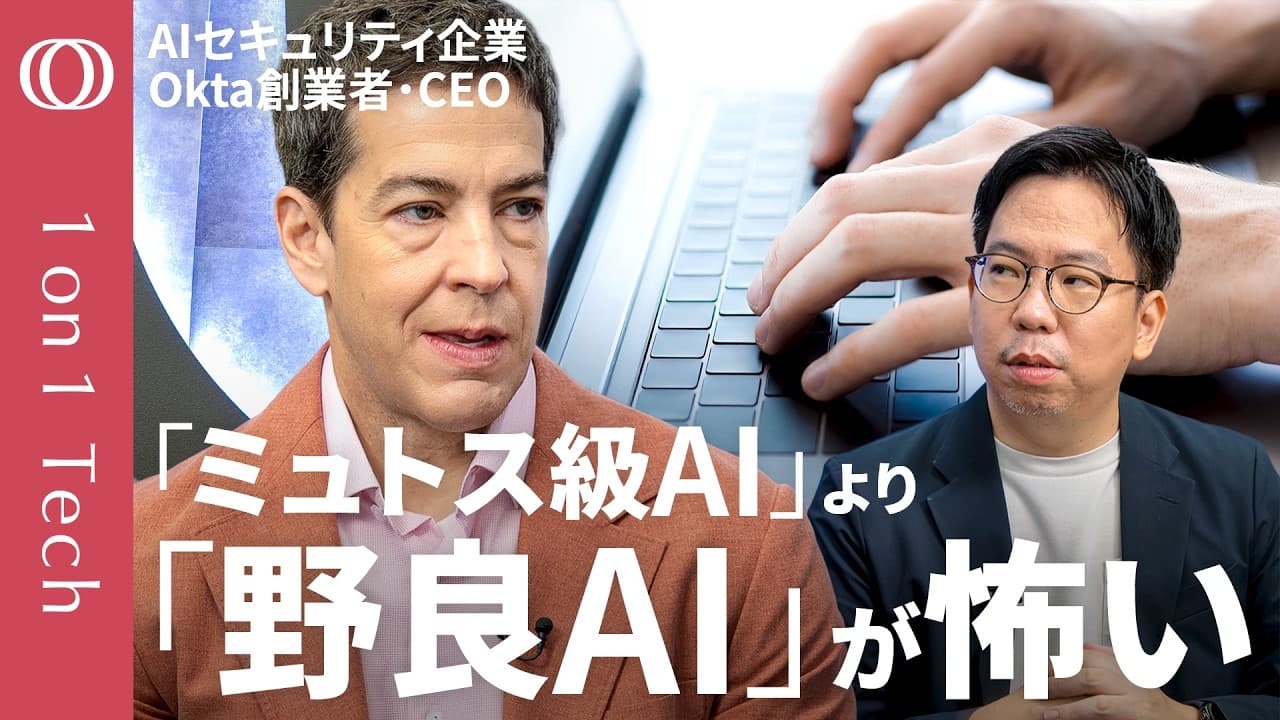
Okta CEO on Securing AI Agents and Shadow AI
TL;DR
Companies should strengthen software patching, adopt phishing-resistant passwordless authentication, and control every AI agent’s identity and permissions. Advanced security models expose additional vulnerabilities, but the underlying defenses remain familiar: verify identities, restrict authorization, monitor connections, manage unauthorized AI use, and provide a kill switch that can immediately stop an agent when its behavior becomes unsafe.
Transcript
One security. Take security. So we are joined by Todd McKinnon, co-founder CEO of Ox. Thank you very much for being here. >> Thanks for having me. I'm excited to have the conversation. >> Yeah, it's the second time for you in Japan. >> Yeah, second time. >> That's what I heard. Okay. How was it? >> It was very It's very good trip. Interest in what ... Read More
Key Insights
- Advanced cybersecurity models are additional vulnerability-discovery tools, not the origin of organizational security weaknesses. McKinnon says vulnerabilities have always been discovered and disclosed, while systems such as Mythos increase the number that defenders can identify and address through existing security processes.
- Software patching is a foundational response to AI-assisted vulnerability discovery. Organizations need infrastructure and operational processes that let them deploy vendor and developer fixes quickly, because identifying more weaknesses provides limited protection when corrected software is not installed across affected systems.
- Passwords are an early target when attackers exploit newly discovered vulnerabilities. McKinnon argues that strong identity verification and authorization can limit account takeover, while companies that continue relying on passwords leave a familiar route available after attackers gain an initial foothold.
- Phishing-resistant passwordless authentication is available but remains insufficiently prioritized by many companies. Its purpose is to prevent an attacker from tricking a user into surrendering reusable login credentials, strengthening both employee and customer access against common identity-based attacks.
- Okta is an identity management and identity security platform designed to help people safely use different technologies. Its products secure employee access, support customer sign-ins, and give information technology and security teams visibility into accounts, permissions, authentication, and activity.
- AI agents create an identity and authorization problem because they connect systems, consume information, and act across organizational boundaries. McKinnon sees an opportunity for Okta to serve as a control plane governing how different agentic systems authenticate and connect with one another.
- Shadow AI is unauthorized AI use inside an organization, and the title states that 47.5 percent of Japanese company employees use it without permission. The risk requires organizational visibility and governance because unmanaged tools may operate beyond the security controls applied to approved technology.
- A kill switch is an immediate containment mechanism for an AI agent whose behavior becomes unsafe or unpredictable. The interview presents rapid disconnection as a necessary safeguard alongside identity controls, monitoring, permissions management, and policies addressing unauthorized AI use.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How should companies respond to AI-discovered security vulnerabilities?
Companies should reinforce the security practices they already know are necessary. McKinnon emphasizes patching systems, deploying software updates quickly, modernizing identity security, verifying users strongly, and controlling authorization. Advanced models can identify additional vulnerabilities, but discovery does not replace remediation. Organizations still need the infrastructure, staffing, and operating discipline required to install fixes and protect accounts before attackers exploit identified weaknesses.
Q: Why does AI vulnerability discovery make password security more urgent?
Attackers can use newly identified software weaknesses as an initial route toward stealing passwords and taking over accounts. McKinnon therefore treats identity security as a core layer of defense rather than a separate concern. Strong verification, carefully managed authorization, and passwordless authentication can reduce reliance on credentials that attackers may steal, reuse, or obtain by deceiving a legitimate user.
Q: What is phishing-resistant passwordless authentication?
Phishing-resistant passwordless authentication is an access method designed so that an attacker cannot simply trick a user into surrendering a reusable password. McKinnon says the necessary technology already exists, but many companies have not prioritized the upgrade for employees or customers. Adopting it strengthens identity verification and addresses the password theft that often follows exploitation of a security vulnerability.
Q: What does Okta do for companies and internet services?
Okta provides identity management and identity security products. These products help employees sign in securely to workplace systems, help people access websites, and allow information technology departments and chief security officers to manage accounts, environments, and permissions. The platform also gives organizations visibility into access activity so they can understand what is happening and maintain appropriate security controls.
Q: Does Mythos create an entirely new cybersecurity threat?
McKinnon does not describe Mythos as turning a world with no vulnerabilities into one with hundreds. Vulnerabilities have always existed and are continually discovered and disclosed. Mythos is an important new tool that can reveal incrementally more weaknesses. Its arrival increases the urgency of remediation, but it primarily reinforces the need for familiar measures such as patching, secure deployment, and identity protection.
Q: Why do AI agents require dedicated identity security?
AI agents need data and connections to become more useful, and organizations are introducing them across operating systems, cloud platforms, vendor products, and internally developed services. Each connection raises questions about identity, permissions, and accountability. McKinnon argues that agentic security must govern how these systems connect, authenticate, receive information, and obtain authority to act across an organization’s technology environment.
Q: What is shadow AI and why is it a corporate risk?
Shadow AI refers to AI tools used inside a company without formal permission or management. The title reports that 47.5 percent of employees at Japanese companies use such unauthorized AI. This creates a governance problem because security teams may lack visibility into which tools are operating, what information they access, and whether established identity, permission, and monitoring controls apply to them.
Q: When should an organization use an AI agent kill switch?
An organization should use a kill switch when an AI agent behaves unpredictably, exceeds its intended authority, or creates a security risk that requires immediate containment. The interview presents the mechanism as a way to stop or disconnect an agent quickly during a crisis. It complements preventive controls such as verified identities, restricted permissions, connection management, monitoring, and governance of approved and unauthorized AI tools.
Summary & Key Takeaways
-
Todd McKinnon argues that advanced cybersecurity models do not transform a previously safe world into a vulnerable one. Vulnerabilities already existed, and new models reveal incrementally more of them. Organizations should respond by improving established defenses, especially rapid software patching, secure deployment practices, strong identity verification, and carefully controlled authorization across their environments.
-
Okta provides identity management and identity security services that help employees access workplace systems, customers sign in to websites, and security teams manage accounts and permissions. McKinnon says passwords remain a prime target after vulnerabilities are exploited, making phishing-resistant passwordless authentication a central defense for organizations modernizing security in response to AI-enabled threats.
-
AI agents create a large identity security challenge because organizations are adding agentic capabilities to operating systems, cloud platforms, vendor products, and internally developed tools. These agents require data and connections to become useful, but those same connections require oversight. Companies also need visibility into shadow AI and mechanisms for immediately stopping unsafe agents.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from TBS CROSS DIG with Bloomberg 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator