What Is Claude Mythos and Why Is It Withheld?
TL;DR
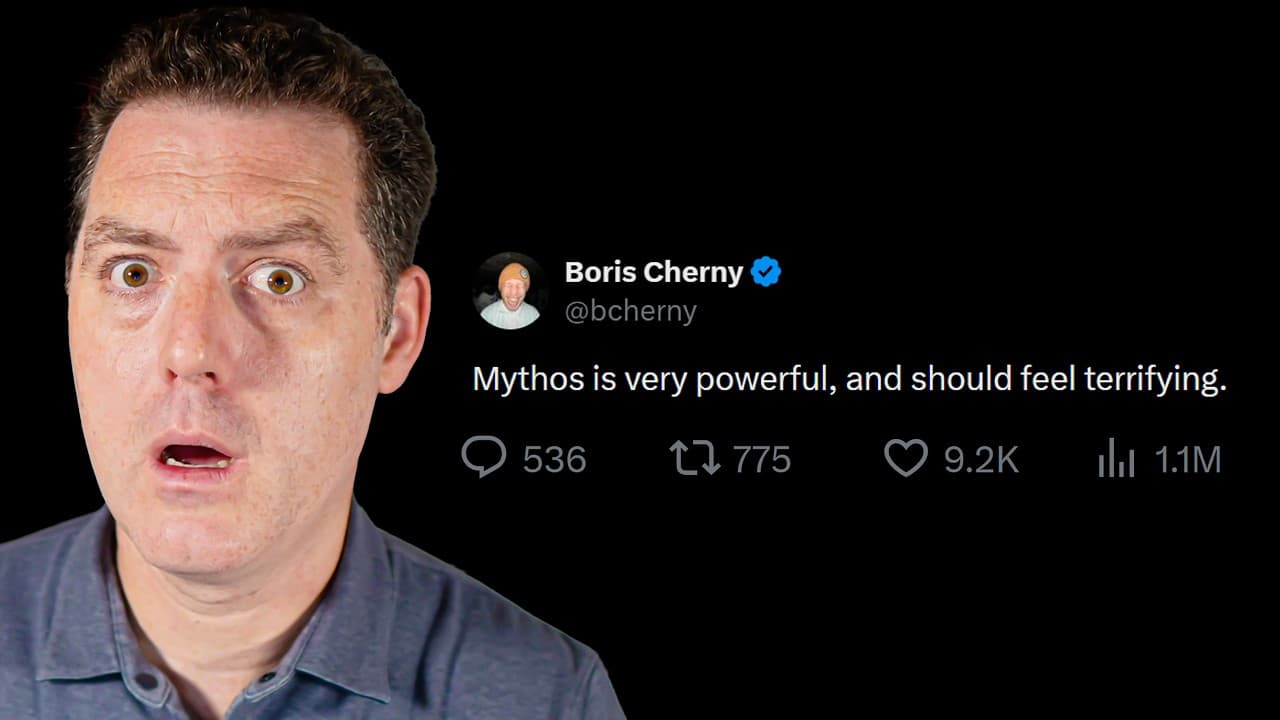
Claude Mythos preview is presented as a frontier Anthropic model whose autonomous vulnerability discovery prompted Project Glasswing and delayed public release. According to the transcript, it found thousands of high-severity and zero-day flaws across major operating systems, browsers, and other software while substantially outperforming Claude Opus 4.6 on several coding benchmarks. The central concern is that such capabilities could strengthen cyber defense while also creating severe security risks.
Transcript
This is going to be a slightly different video today. Not only because Anthropic announced Mythos, their rumored model, the next generation of artificial intelligence, the best AI model on the planet by far, but because I felt the need to record this late at night on my vacation. That's how big of a deal this is. And so, why did I need to record th... Read More
Key Insights
- Project Glasswing is an urgent defensive initiative involving Anthropic and selected technology, cybersecurity, financial, and infrastructure organizations. The transcript says these partners received access to Mythos capabilities so they could find vulnerabilities and strengthen critical software before similarly powerful tools become broadly available.
- Claude Mythos preview is described as an autonomous vulnerability researcher that found thousands of high-severity and zero-day flaws. The reported targets included every major operating system, every major web browser, and other important software, raising concerns about economies, public safety, and national security.
- A zero-day vulnerability is described as a previously undiscovered software weakness. The transcript argues that finding thousands is especially significant because attackers can chain multiple weaknesses together, potentially bypassing protections and gaining control over systems that support health care, finance, infrastructure, and other critical functions.
- The OpenBSD finding is presented as a 27-year-old vulnerability in an operating system known for security hardening. According to the transcript, the flaw allowed an attacker to remotely crash any machine running the operating system simply by connecting to it, despite OpenBSD's use in firewalls and critical infrastructure.
- The Linux kernel result is described as an autonomous chain of several vulnerabilities. The transcript says this chain could let an attacker move from ordinary user access to complete machine control, illustrating how combining multiple flaws can produce consequences more serious than exploiting one vulnerability independently.
- Mythos preview scored 77.8 on SWE-bench Pro, compared with 53.4 for Opus 4.6. The transcript also reports scores of 82 versus 65.4 on Terminal-Bench 2.0, 59 versus 27 on SWE-bench Multimodal, and 94 versus 80 on SWE-bench Verified.
- Mythos is reportedly a 10 trillion parameter model produced through Anthropic's latest training run and the latest generation of Nvidia Blackwell hardware. Its training mixture included public internet information, public and private datasets, and synthetic data generated by other models, followed by substantial post-training and fine-tuning.
- Anthropic's stated risk conclusion is that catastrophic risks remain low despite Mythos being significantly more capable than Claude Opus 4.6. The transcript also describes the model as well aligned and willing to follow alignment, while emphasizing that extreme capability still warrants caution because a single catastrophe could be consequential.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: What is Claude Mythos preview?
Claude Mythos preview is described as Anthropic's new frontier model and a major departure from incremental Claude Opus upgrades. The transcript portrays it as exceptionally capable at coding, terminal use, software engineering, and autonomous vulnerability discovery. It has not been released publicly, and Anthropic reportedly shared its capabilities with selected Project Glasswing partners to strengthen critical software before wider availability is considered.
Q: Why has Anthropic not released Claude Mythos publicly?
Anthropic reportedly withheld Claude Mythos because its software and cybersecurity capabilities could be dangerous if deployed without adequate preparation. The transcript says no existing software may be secure enough to withstand determined attacks using the model. Project Glasswing therefore gives selected organizations an opportunity to discover weaknesses and harden critical systems before these capabilities proliferate to actors who may not deploy them safely.
Q: What is Project Glasswing?
Project Glasswing is described as a defensive cybersecurity initiative bringing together Anthropic, Amazon Web Services, Apple, Broadcom, Cisco, CrowdStrike, Google, JP Morgan, the Linux Foundation, Microsoft, Nvidia, and Palo Alto Networks. It was formed after Anthropic observed capabilities in a new frontier model that could reshape cybersecurity. Its purpose is to apply those capabilities defensively and strengthen critical software before comparable tools spread more widely.
Q: What vulnerabilities did Claude Mythos discover?
The transcript says Claude Mythos preview found thousands of high-severity and zero-day vulnerabilities across major operating systems, web browsers, and other important software. Specific examples included a 27-year-old OpenBSD vulnerability, a 16-year-old FFmpeg vulnerability, and several Linux kernel weaknesses that the model chained together. That Linux chain reportedly allowed escalation from ordinary user access to complete control of a machine.
Q: How autonomous was Claude Mythos during security research?
Claude Mythos reportedly discovered vulnerabilities almost entirely autonomously, with little or no human guidance beyond being directed to perform the task. The transcript highlights this autonomy because it changes the scale of security research. An AI system can inspect software continuously and conduct many investigations in parallel, while human researchers cannot sustain the same around-the-clock pace or degree of parallelized analysis.
Q: How did Mythos compare with Opus 4.6 on benchmarks?
Mythos substantially exceeded Opus 4.6 on every benchmark quantified in the transcript. It scored 77.8 versus 53.4 on SWE-bench Pro, 82 versus 65.4 on Terminal-Bench 2.0, 59 versus 27 on SWE-bench Multimodal, and 94 versus 80 on SWE-bench Verified. The transcript also says Mythos achieved greater accuracy while using fewer average tokens per BrowseComp task, indicating improved efficiency.
Q: How was Claude Mythos reportedly trained?
Claude Mythos preview was reportedly trained on a proprietary mixture of publicly available internet information, public and private datasets, and synthetic data generated by other models. Anthropic used ClaudeBot to collect permitted public web data while following robots.txt and avoiding protected pages. Training also involved deduplication, classification, other cleaning and filtering methods, substantial post-training, fine-tuning, and reinforcement learning aligned with Claude's Constitution.
Q: Why could Mythos affect cybersecurity beyond coding benchmarks?
Mythos could affect cybersecurity because software supports operating systems, browsers, servers, financial systems, health systems, and critical infrastructure. The transcript argues that a model capable of autonomously finding and chaining large numbers of undiscovered vulnerabilities could expose systems faster than people can repair them. The same capability can support defenders through Project Glasswing, but it could also create severe economic, public-safety, and national-security consequences if misused.
Summary & Key Takeaways
-
Anthropic reportedly organized Project Glasswing with major technology, financial, cybersecurity, and infrastructure organizations after observing Claude Mythos preview's advanced vulnerability-discovery capabilities. The initiative gives selected partners access to defensive capabilities so they can identify weaknesses, harden critical software, and prepare before comparable offensive capabilities become more widely available to potentially unsafe actors.
-
The transcript says Mythos discovered thousands of high-severity and zero-day vulnerabilities with little human guidance. Examples included a 27-year-old OpenBSD flaw, a 16-year-old FFmpeg flaw, and a chain of Linux kernel vulnerabilities that could elevate ordinary user access into complete control of a machine, demonstrating broad autonomous cybersecurity capability.
-
Mythos is described as both substantially more capable and more efficient than Claude Opus 4.6 across coding, terminal, multimodal, and verified software-engineering benchmarks. The model reportedly combines large-scale training, synthetic data, cleaning and filtering, post-training, reinforcement learning, and alignment with Claude's Constitution, although Anthropic has not released it publicly yet.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from Matthew Berman 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator