How to Reduce Ransomware and Emerging TTP Risks
TL;DR
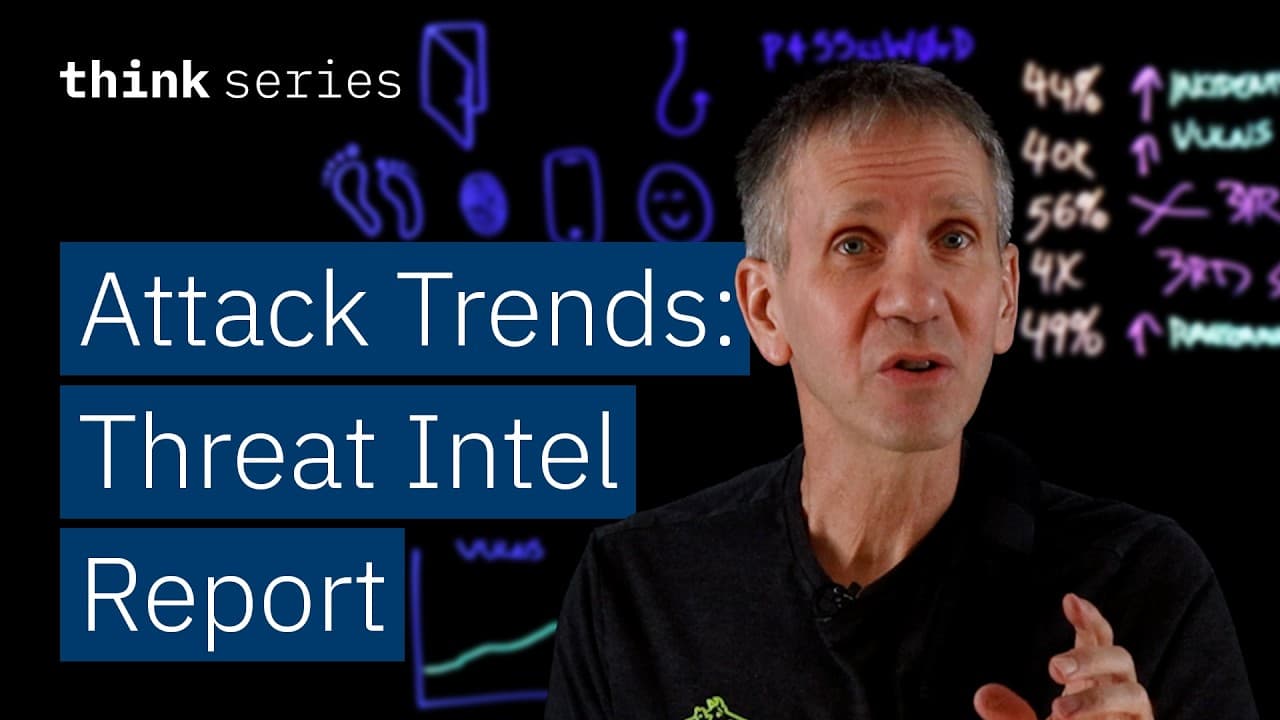
Continuously discover and test vulnerabilities, protect identity with multi-factor authentication and passkeys, secure secrets, and establish strong AI governance. The report highlights rising vulnerability exploitation, nearly 40,000 new vulnerabilities, growing third-party compromise, converging attacker techniques, and a 49% increase in ransomware groups as urgent reasons to strengthen these defenses.
Transcript
Let's say you're out for your morning run in the 20-degree chill at dawn. Suddenly you come upon a patch of ice and your run turns into an ice skating exhibition instead. It would have been nice if you'd had a threat intelligence report that warned you in advance where the dangerous spots would be. That kind of information could save you from going... Read More
Key Insights
- Vulnerability exploitation incidents rose sharply by 44%, showing that exposed software weaknesses are becoming a more important route into systems. Defenders should therefore make continuous vulnerability discovery and testing a core security activity rather than treating assessment as an occasional project.
- Nearly 40,000 new vulnerabilities were reported, which was 13,000 more than during the previous year. The size and direction of this increase indicate that organizations face a growing volume of weaknesses requiring prioritization, review, testing, and remediation.
- Unauthenticated exploitation affected 56% of the vulnerabilities tracked, and this share remained largely unchanged for a third consecutive year. Such weaknesses let attackers enter without crafting phishing messages, stealing passwords, or bypassing multi-factor authentication, while also producing fewer credential-associated forensic traces.
- Remote code execution can result from insecure application behavior, including allowing unauthenticated users to upload arbitrary files. In the cited app-server example, an attacker could supply chosen code for the target system to execute, potentially producing full system compromise without prior permission.
- Supply chain and third-party compromises nearly quadrupled over five years. Attackers increasingly target locations where software is developed or deployed, including SaaS integrations, because compromising ingredients or dependencies can undermine the wider software system built from them.
- Attacker tactics, techniques, and procedures are converging across nation-state, ransomware, and other financially motivated operations. North Korean nation-state actors using information stealers illustrate how tools once used predominantly by cybercriminals now appear across previously distinct categories of attackers.
- Ransomware groups increased by 49% compared with the previous year, with smaller and more transient operators driving lower-volume campaigns. AI and ransomware-as-a-service tools reduce the barrier to launching attacks, making operators more dispersed and consequently harder to track.
- Effective preparation requires identity protection, AI governance, secrets management, and continuous security testing. Recommended measures include multi-factor authentication, passkeys, a secrets vault for API and cryptographic keys, appropriate AI policies and tools, regular code reviews, penetration tests, and ongoing vulnerability discovery.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How should organizations respond to emerging ransomware and TTP risks?
Organizations should first review the full threat intelligence report to understand the risks beyond its highlighted findings. They should treat identity as critical infrastructure by requiring multi-factor authentication and passkeys, manage API and cryptographic keys through a secrets vault, establish strong AI governance with appropriate policies and tooling, and continuously discover vulnerabilities through regular code reviews, penetration tests, and ongoing testing.
Q: Why are unauthenticated vulnerabilities especially dangerous?
Unauthenticated vulnerabilities are dangerous because attackers can exploit them without identifying themselves or possessing valid credentials. They do not need to create phishing emails, steal passwords, or bypass multi-factor authentication. Attacks that are not associated with credentials can also leave fewer forensic footprints, making investigation and attribution harder. The report found that 56% of tracked vulnerabilities could be exploited without authentication.
Q: How can arbitrary file uploads lead to remote code execution?
An application that permits unauthenticated users to upload arbitrary files can allow an attacker to place malicious code on the target system. In the app-server example discussed, this behavior led to remote code execution, meaning the attacker could send code of their choice and cause the system to run it without permission. In some cases, that capability can produce full system compromise.
Q: Why are software supply chains becoming a larger security risk?
Supply chain and third-party compromises nearly quadrupled over five years because attackers are targeting places where software is developed and deployed. SaaS integrations and other third-party components can become pathways into a broader system. Compromising an ingredient used to build or operate software can weaken everything that depends on it, creating a fragile environment vulnerable to wider compromise.
Q: How are nation-state and ransomware attacker techniques converging?
Nation-state actors, ransomware operators, and other financially motivated attackers increasingly use overlapping tactics, techniques, and procedures. These groups previously tended to operate in more distinct ways, but those boundaries are becoming less clear. One example is North Korean nation-state actors using information stealers, software designed to collect passwords and other secrets that was once used predominantly by cybercriminals.
Q: Why did the number of ransomware groups increase by 49%?
The 49% increase in ransomware groups was driven by smaller, transient operators running more low-volume campaigns. AI and ransomware-as-a-service tools have made ransomware attacks easier to operate by lowering the barrier to entry. The transcript describes AI helping identify targets, choose exploits, launch attacks, and handle collections. More dispersed operators are also harder for defenders and investigators to track.
Q: How should organizations protect identity and sensitive keys?
Organizations should treat identity as critical infrastructure and eliminate easy access routes for attackers. The recommended controls are multi-factor authentication and passkeys. API keys, cryptographic keys, and similar secrets should be managed through a secrets vault. These measures strengthen access controls and reduce the free passes attackers may otherwise receive when identities or sensitive keys are insufficiently protected.
Q: What continuous security testing does the report recommend?
Organizations should discover and test for vulnerabilities continuously instead of assuming that existing security measures remain sufficient. The recommended practices include regular code reviews and penetration tests, supported by ongoing vulnerability discovery. This approach responds directly to the sharp rise in incidents caused by vulnerability exploitation and the nearly 40,000 new vulnerabilities reported, which was 13,000 more than the previous year.
Summary & Key Takeaways
-
Vulnerability exploitation caused 44% more incidents, while nearly 40,000 new vulnerabilities were reported, 13,000 more than in the previous year. Of the tracked vulnerabilities, 56% could be exploited without authentication, allowing attackers to avoid phishing, credential theft, and multi-factor authentication while leaving fewer credential-linked forensic footprints.
-
Supply chain and third-party compromises nearly quadrupled over five years as attackers increasingly targeted software development and deployment through SaaS integrations and related pathways. At the same time, tactics, techniques, and procedures began converging across nation-state, ransomware, and financially motivated groups, including North Korean actors adopting information-stealing software previously associated mainly with cybercriminals.
-
Ransomware groups increased by 49% from the previous year, driven by smaller, transient operators conducting lower-volume campaigns. AI and ransomware-as-a-service tools lowered barriers to entry and helped disperse attackers. Recommended defenses include protecting identity, securing keys in a secrets vault, governing AI, reviewing code, conducting penetration tests, and testing vulnerabilities continuously.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from IBM Technology 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator