How Should US Organizations Prepare for GDPR?
TL;DR
US organizations should prepare for GDPR by identifying personal data broadly and consistently, then assessing the IT and security capabilities needed to protect it. Non-compliance can trigger fines based on global revenue, disrupt transfers of personal data outside the European Union, prompt lawsuits and regulatory investigations, and damage customer trust and reputation.
Transcript
Thank you, James. And welcome everybody to this session on the General Data Protection, uh, Regulation and the last session of the day, uh, as well. One billion dollars, is that a lot of money? Maybe. It depends. It depends. Are you a consultant? It's a-- Or a lawyer. You can be one or the other, and it depends always works. It does. It depends on ... Read More
Key Insights
- GDPR fines have two tiers based on global top-line revenue and fixed euro amounts. Penalties can reach 2 percent or 10 million euros, whichever is greater, or 4 percent or 20 million euros, whichever is greater, depending on the violation tier.
- GDPR compliance requires new IT and security capabilities that cost money and may force organizations to lower the priority of other initiatives. Privacy work can struggle for executive attention because it focuses on avoiding future costs rather than directly generating revenue or reducing current expenses.
- Restrictions on transferring personal data outside the European Union can threaten an organization’s European operations. Companies with data flows from the EU to the United States or other global locations must consider how losing permission for those transfers could affect their ability to conduct business.
- GDPR non-compliance can expose organizations to individual lawsuits and investigations by data protection authorities in EU member states. Responding to information requests, inquiries, and depositions can consume significant time, energy, and money while diverting employees from their regular responsibilities.
- Adverse media coverage can extend the consequences of a privacy violation beyond the original incident. Reports may be repeated by additional outlets, and organizations with earlier compliance failures can continue to be named later as examples in stories about new privacy problems.
- Customer trust is central to data privacy because organizations depend on people being comfortable sharing personal data for stated purposes. Non-compliance and reputational damage can weaken that comfort, making privacy governance important beyond the immediate risks of fines, litigation, and investigations.
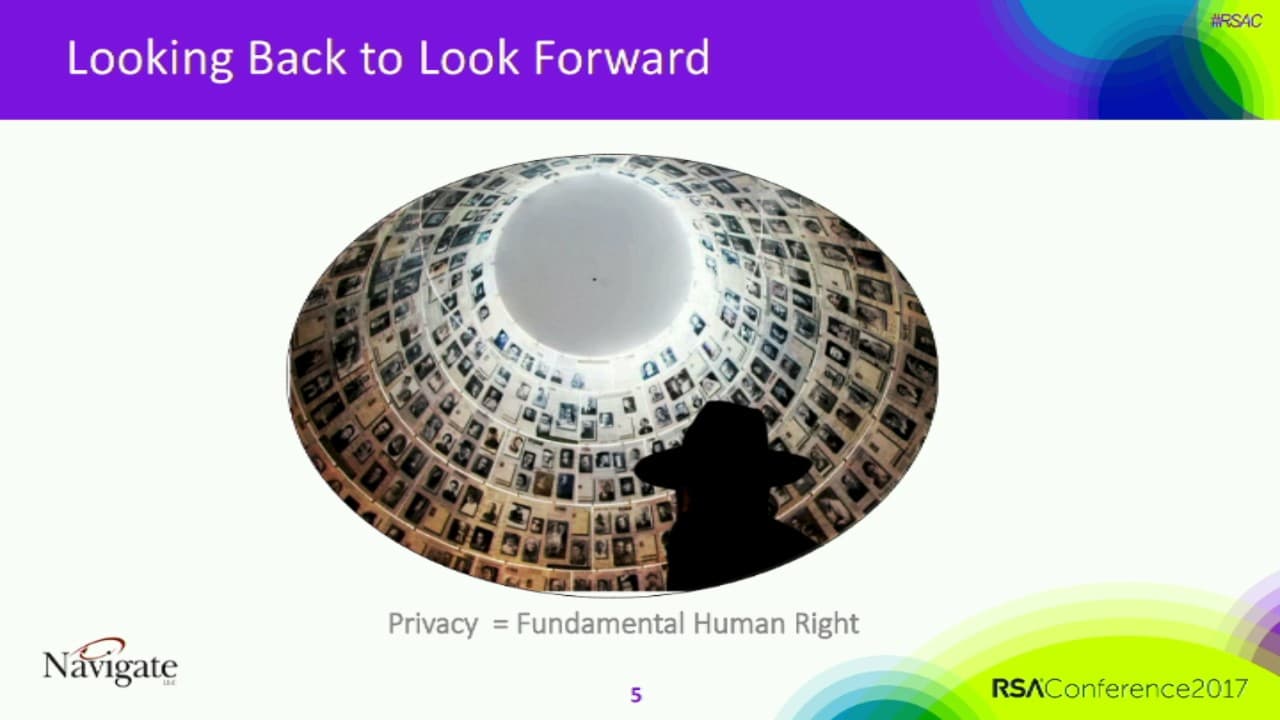
- European data privacy is treated as a fundamental human right, with the speaker tracing regulators’ strong commitment to experiences surrounding World War II. The presentation compares the seriousness of this European view with the importance attached to freedom of speech in the United States.
- Personal data is defined broadly as information attributable to an identified or identifiable individual. Public availability does not remove information from that category, and examples identified in the presentation include email addresses, dates of birth, IP addresses, and other identifiers.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How should US organizations begin preparing for GDPR?
US organizations should begin by establishing a clear and consistent definition of personal data across marketing, technology, security, privacy, and other business functions. They should then assess the new IT and security capabilities required for compliance, determine the necessary funding, and explain to executives that failures can create financial, operational, legal, regulatory, media, and reputational consequences.
Q: What GDPR fines can organizations face?
GDPR has two described fine tiers. One can reach 2 percent of an organization’s global top-line revenue or 10 million euros, whichever is greater. The other can reach 4 percent of global top-line revenue or 20 million euros, whichever is greater. A company with 25 billion dollars in top-line revenue could therefore face a potential 1 billion dollar fine at the 4 percent level.
Q: Why does GDPR compliance require executive attention?
GDPR compliance requires executive attention because the financial stakes can be tied to global top-line revenue, while the required IT and security capabilities cost money and may displace other priorities. Executives also need to consider interrupted international data flows, individual lawsuits, regulatory investigations, adverse media coverage, reputational harm, and reduced customer trust, not just the direct fine exposure.
Q: How can GDPR violations disrupt international business operations?
GDPR violations can result in an organization losing the ability to transfer personal data outside the European Union. For a global company that moves data from the EU to the United States or other operational locations, such a restriction could severely damage or potentially end its European business. Data-transfer continuity is therefore a core operational concern, not merely a technical compliance issue.
Q: What counts as personal data under GDPR?
Personal data should be understood broadly as essentially any data that can be attributed to an identified or identifiable individual. The presentation identifies email addresses, dates of birth, IP addresses, and other identifiers as examples. Information does not stop being personal data simply because someone can locate it through Google or another publicly accessible source.
Q: Why must departments share one definition of personal data?
Departments must share one definition because marketing leaders, technology executives, security officers, and other functions may interpret personal data differently. GDPR compliance depends on recognizing which information falls within scope throughout the organization. According to the presentation, the risk of non-compliance tracks directly with an inconsistent understanding, so a clear common definition is a foundational readiness requirement.
Q: What non-financial consequences can GDPR non-compliance cause?
Non-financial consequences include individual lawsuits, investigations by data protection authorities in EU member states, disruption of personal-data transfers, adverse media coverage, reputational damage, and declining customer trust. Investigations can also consume considerable time and energy through information gathering, inquiries, and depositions, pulling employees away from their regular work even before any final regulatory outcome occurs.
Q: Why is data privacy treated so seriously in Europe?
European regulators treat data privacy as a human right or fundamental human right, not as a casual policy preference. The speaker connects this strong view to World War II and to the consequences that personal information about religion, health status, or political affiliation could have during that period. The presentation compares its seriousness with how freedom of speech is regarded in the United States.
Summary & Key Takeaways
-
GDPR raises substantial financial and operational risks for organizations doing business in the European Union. Its two fine tiers can reach 2 percent of global top-line revenue or 10 million euros, and 4 percent or 20 million euros, with the greater amount applying in each respective tier.
-
Compliance requires organizations to develop new IT and security capabilities, which demand funding and may displace other priorities. Business leaders should also recognize that violations can threaten personal-data transfers outside the European Union, consume employee time during regulatory investigations, invite individual lawsuits, and generate continuing adverse media attention.
-
A consistent, organization-wide definition of personal data is essential to GDPR readiness. The regulation treats the concept broadly as data attributable to an identified or identifiable individual, including publicly accessible information, IP addresses, and other identifiers. Differing interpretations among marketing, security, technology, and other teams increase non-compliance risk.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from RSAC Cybersecurity 📚






Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator