How Should Society Manage Cryptographic Risk?
TL;DR
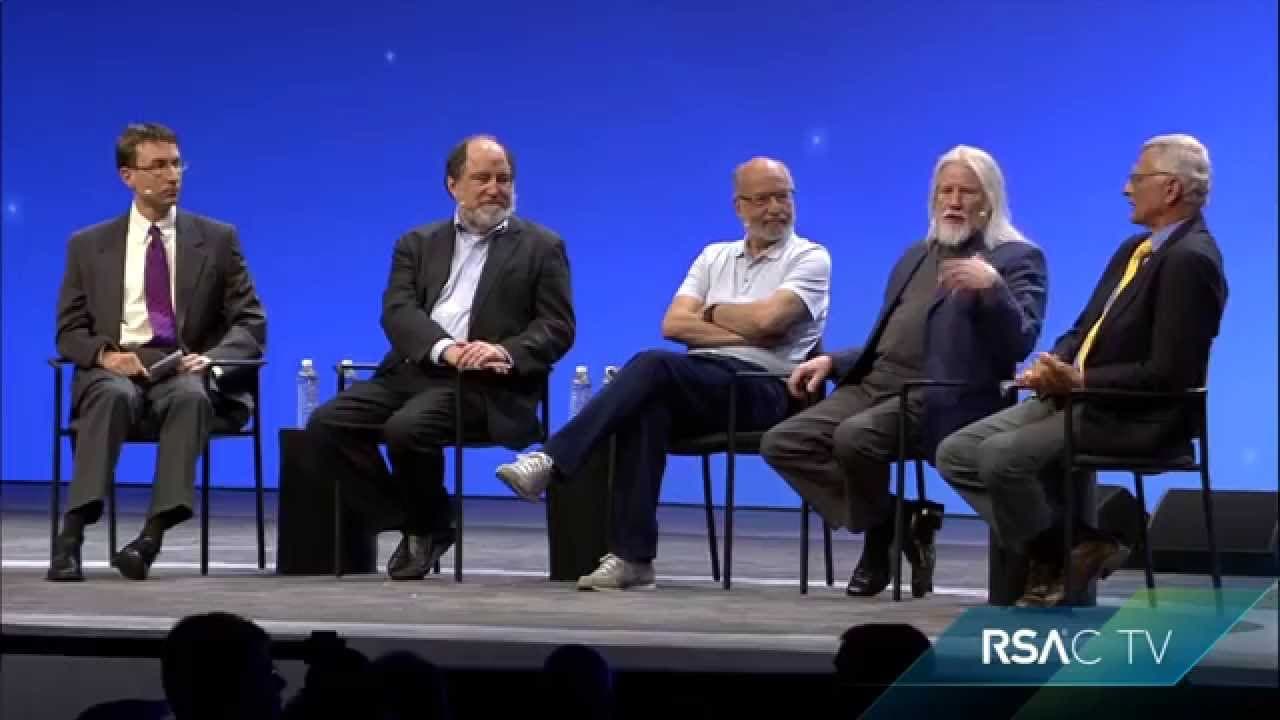
Fully secure systems do not exist, so society must manage technological risk through layered defenses, realistic spending, careful implementation, and limited trust. Cryptography remains essential, but attackers often bypass it through vulnerable software, privileged services, insecure device setup, or unexpected channels such as tiny changes in connected lighting.
Transcript
The massive economic growth associated with the Industrial Revolution brought extreme environmental problems. The massive economic growth associated with today's technology industry has brought tremendous benefits along with corresponding problems, the electronic form of toxic waste, the security vulnerabilities that we face today. Our ability as a... Read More
Key Insights
- Technological growth creates security costs alongside benefits, and society's ability to benefit from technology depends on managing vulnerabilities rather than ignoring them. The panel compares these vulnerabilities to electronic toxic waste produced by the expanding technology industry.
- Digital transparency changes relationships between participants, much as newly extended visibility could change interactions between predators and prey. Ronald Rivest uses this analogy to suggest that the digital revolution has placed society in a fundamentally altered environment.
- Discrete logarithm research showed a qualitative improvement for finite fields of small characteristic. The result did not produce a polynomial-time algorithm, but it substantially improved the running time for solving the problem in those particular finite fields.
- Fully secure systems do not exist and will not exist, according to Adi Shamir's first law of security. Security planning must therefore accept residual vulnerability and concentrate on achieving protection that is sufficient for realistic threats and resources.
- Cryptography is often bypassed rather than broken, according to Shamir's second law. Attackers can exploit surrounding software, installation processes, trusted privileges, or physical channels without defeating the mathematical protection at the center of a system.
- Stronger security becomes disproportionately expensive as protection approaches completeness. Shamir summarizes this economic problem by saying that halving vulnerability requires doubling cost, making the final bugs and the most sophisticated attacks exceptionally difficult to address.
- Connected lighting can become a covert information channel through brightness changes that are too small and rapid for the human eye to notice. A receiver outside a secure perimeter could detect those changes and recover information available inside it.
- Extensive vendor control transfers trust away from users and can create new intrusion paths. Diffie argues that businesses seek systems that protect customers from outsiders without necessarily protecting customers from the businesses themselves, producing conflicts over configuration and recording.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: Why can cryptography fail without being directly broken?
Cryptography can fail because attackers may bypass the protected algorithm and exploit the surrounding system. The transcript identifies vulnerable software, insecure installation, privileged management access, and physical leakage channels as examples. An attacker therefore may obtain passwords, alter configurations, or extract information without solving the underlying mathematical problem or demonstrating that the cryptographic construction itself is defective.
Q: Why are fully secure systems considered impossible?
Fully secure systems are considered impossible because practical systems contain many interacting components, implementation choices, users, and trust relationships. Adi Shamir argues that complete security does not exist and will not exist. The practical objective is consequently good-enough security, with defenses chosen according to realistic attackers, acceptable residual vulnerability, and the time and effort an organization can reasonably spend.
Q: How does the cost of security change as vulnerability falls?
Security becomes increasingly expensive as organizations try to eliminate the remaining vulnerability. Shamir states the relationship as a rule: halving vulnerability requires doubling cost. Removing most software bugs or stopping most attackers can be comparatively manageable, but finding the last bug or resisting the most sophisticated NSA-type attack may demand an unreasonable amount of time, money, and effort.
Q: How can connected lighting leak protected information?
Connected lighting can leak information by rapidly varying its brightness between nearby levels, such as one hundred percent and ninety-five percent. The human eye may not notice these changes, but an external receiver can detect them. If the lighting controller can access information inside a secure perimeter, those variations can encode and transmit that information to someone positioned outside the perimeter.
Q: What security problem can occur during smart-light setup?
A smart-light installation can expose the local Wi-Fi password during its setup process. In the example discussed by Shamir, installation creates a temporary unsecured Wi-Fi system, and the password is then sent to the lighting controllers without encryption. Anyone monitoring the communication during that setup period could capture the password and potentially gain access to the broader network.
Q: Why does Whitfield Diffie favor stronger defensive security?
Diffie argues that static and defensive protection has been underfunded and undervalued while security practice shifted toward scanning, malware filtering, patch management, and other dynamic responses. He suggests that the current security problems might have been less severe with greater investment in defensive controls. Dynamic management also gives numerous outside parties privileges that users cannot easily understand or audit.
Q: What trust problems arise when vendors manage user systems?
Vendor-managed systems require users to transfer substantial trust to computer makers, application providers, and network businesses. Users may have little ability to understand or audit the privileges these parties receive. Diffie argues that commercial interests can conflict with customer control, and the access demanded by trusted businesses can also become a gateway for intruders whom neither the customer nor vendor intended to admit.
Q: What cryptographic research development did Ronald Rivest highlight?
Rivest highlighted Antoine Joux's result on the discrete logarithm problem for finite fields of small characteristic. He described it as a qualitative improvement that greatly reduced the required running time for those fields, while emphasizing that it was not a polynomial-time algorithm. He presented the advance as a possible sign of further progress in discrete logarithms or factoring.
Summary & Key Takeaways
-
The panel connects technological growth with security vulnerabilities, describing them as a form of electronic toxic waste that society must manage. Ronald Rivest compares the digital revolution to a newly transparent environment in which visibility transforms interactions, while also identifying improved discrete logarithm algorithms as a research development worth watching.
-
Adi Shamir argues that perfect security is unattainable, cryptography is more likely to be bypassed than directly broken, and increasingly strong protection becomes disproportionately expensive. His Internet of Things example shows how an automated lighting system can expose a Wi-Fi password during setup and covertly leak protected information through rapid brightness changes.
-
Whitfield Diffie contends that static, defensive security has been undervalued amid growing reliance on scanning, filtering, patching, and external system management. These arrangements require users to trust vendors with extensive privileges, creating conflicts between businesses and customers while opening pathways that unintended intruders can exploit. Ed Giorgio emphasizes the importance of code making.
-
Key Insights summary omitted due to field ordering constraints.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from RSAC Cybersecurity 📚






Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator