Malware: How Do You Diagnose and Clean Up a Hacked Site?
TL;DR
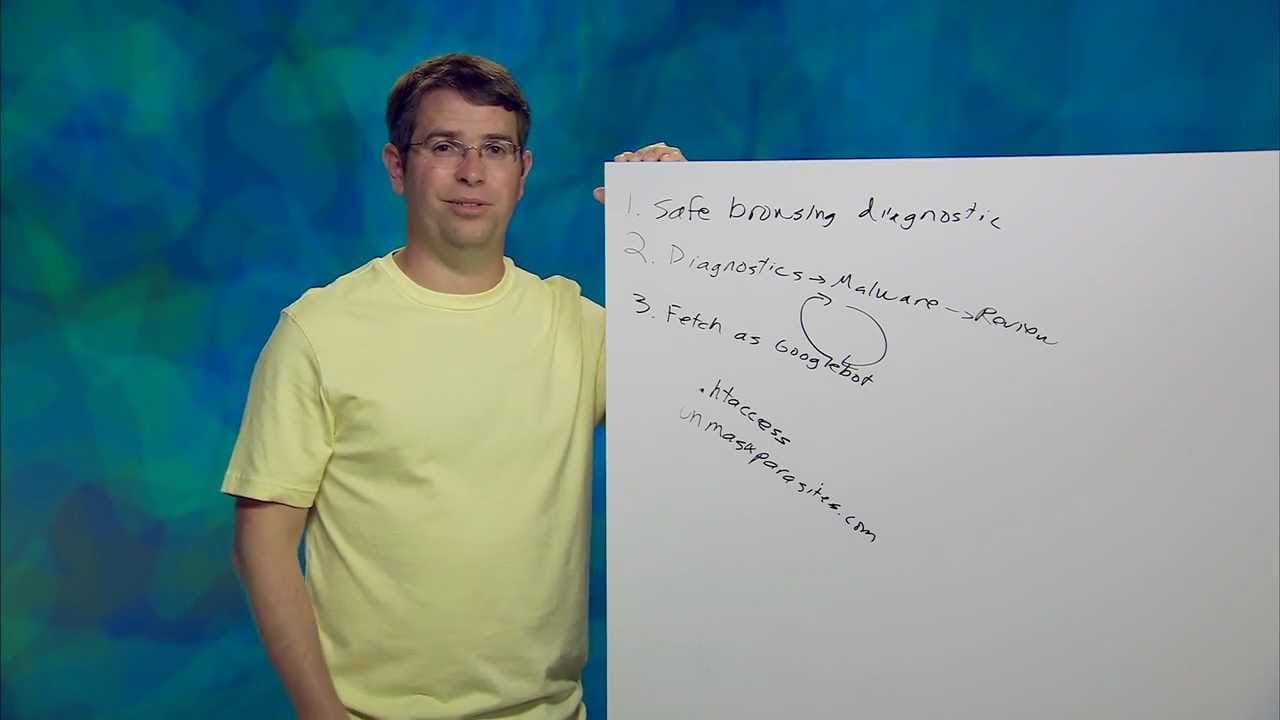
To diagnose and clean up malware, check the affected URL with Google’s Safe Browsing Diagnostic Page, remove infected or third-party content, inspect the returned page with Fetch as Googlebot, and request a malware review through Google’s Webmaster Tools. The review can take several hours but often happens relatively quickly. Read on for specific tools, likely infection points, and practical recovery steps.
Transcript
MATT CUTTS: OK. We've got a neat, interesting topic today. Although, if you're watching this video, you're probably angry and frustrated, and I'll apologize in advance for that. Today, we want to talk about malware and hacked sites. You would not believe how common it is. I don't mind telling you that Donald Trump has had a website hacked. Al Gore ... Read More
Key Insights
- Malware infections are common, affecting even high-profile figures like Donald Trump and Al Gore. It is crucial to prevent showing malware to users.
- Google offers a Safe Browsing Diagnostic Page to check if a URL is infected with malware, providing detailed statistics and infection status.
- Site owners should register their sites with Google's Webmaster Tools to request a malware review after cleaning up infected content.
- Fetch as Googlebot allows site owners to see what Googlebot sees, helping identify hidden malware that might not be visible in the source code.
- Common malware entry points include HT access files and SQL injection vulnerabilities. Site owners should ensure their systems are up-to-date to prevent such attacks.
- Strong, random passwords are essential for site security. Weak passwords like '123456' or 'password' should be avoided.
- Unmaskparasites.com is a valuable resource for understanding current malware attacks and trends.
- Google is committed to protecting users from malware, offering several tools to help webmasters clean up infected sites and prevent future attacks.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: How do you diagnose and clean up malware on a hacked site?
Check the site or a specific URL with Google’s Safe Browsing Diagnostic Page and review the infection information it provides. Remove infected content or stop loading malicious third-party ads, scripts, or JavaScript, then use Fetch as Googlebot to inspect what the server actually returns. After cleaning the site, request a malware review through Google’s Webmaster Tools.
Q: What is Google’s Safe Browsing Diagnostic Page?
The Safe Browsing Diagnostic Page lets you enter a URL or domain to see whether Google believes it is infected with malware. It also provides statistics and other information about malware detected on the domain. The results may reveal that the infection comes from third-party content rather than the site itself.
Q: How can a site owner request a malware review from Google?
Register the site in Google’s Webmaster Tools and prove that you own or control it. After cleaning the site, open the diagnostics page, select the malware tab, and request a review. Google then provides examples of URLs it believes contain malware, including additional examples if the scan still finds an infection.
Q: How long does a Google malware review take?
A requested review is not an instantaneous or real-time scan. Matt Cutts says it often happens in roughly an hour’s timeframe, although it can take several hours. This allows site owners to iterate relatively quickly when Google continues to identify infected URLs.
Q: What is Fetch as Googlebot, and how does it help detect malware?
Fetch as Googlebot is a Google Webmaster Tools feature that retrieves a verified page as Googlebot and shows exactly what the server returned. It reports details such as a 301 redirect and the page’s actual content. This can expose malicious material shown to Googlebot but hidden from regular users or absent from apparently clean source files.
Q: Where should site owners look for hidden malicious changes?
Site owners should inspect HT access files and check for SQL injection caused by URL parameters or inputs that were not properly sanitized. They should also examine what the browser or Googlebot actually receives, because mod rewrite rules, HT access settings, or another intermediate step may inject malware even when the source code looks clean.
Q: What should you do if malware comes from a third-party domain?
The Safe Browsing Diagnostic Page may show that an external domain supplying ads, scripts, JavaScript, or other included content is infected. Remove that third-party content or stop loading it. Matt Cutts says the malware warning should then clear relatively quickly.
Q: How can site owners reduce the risk of another malware infection?
Keep the site’s software up to date and patch WordPress if that is the platform being used. For any other content management system, use its most recent version. Site owners should also sanitize URL parameters and inputs to reduce exposure to SQL injection.
Summary & Key Takeaways
-
Matt Cutts discusses the prevalence of malware and hacked sites, emphasizing the importance of preventing malware exposure to users. He introduces Google's Safe Browsing Diagnostic Page, which helps identify infected URLs and provides detailed statistics on malware presence.
-
Site owners are encouraged to register with Google's Webmaster Tools to request a malware review after cleaning their sites. The Fetch as Googlebot tool allows owners to see what Googlebot sees, helping identify hidden malware.
-
Common vulnerabilities include HT access files and SQL injection. Keeping systems updated and using strong passwords are crucial for security. Google offers several tools and resources to assist webmasters in cleaning and securing their sites.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from Google Search Central 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator