Why Did Qualcomm's Humanoid Robot Collapse?
TL;DR
The humanoid robot reportedly collapsed because a communication glitch activated a designed safety response, although the incident exposed the gap between controlled demonstrations and reliable deployment. Its fall, following delivery of a chip promoted as production ready, shows why businesses need fallbacks, human checkpoints, and realistic expectations whenever AI moves from simulation into unpredictable physical environments.
Transcript
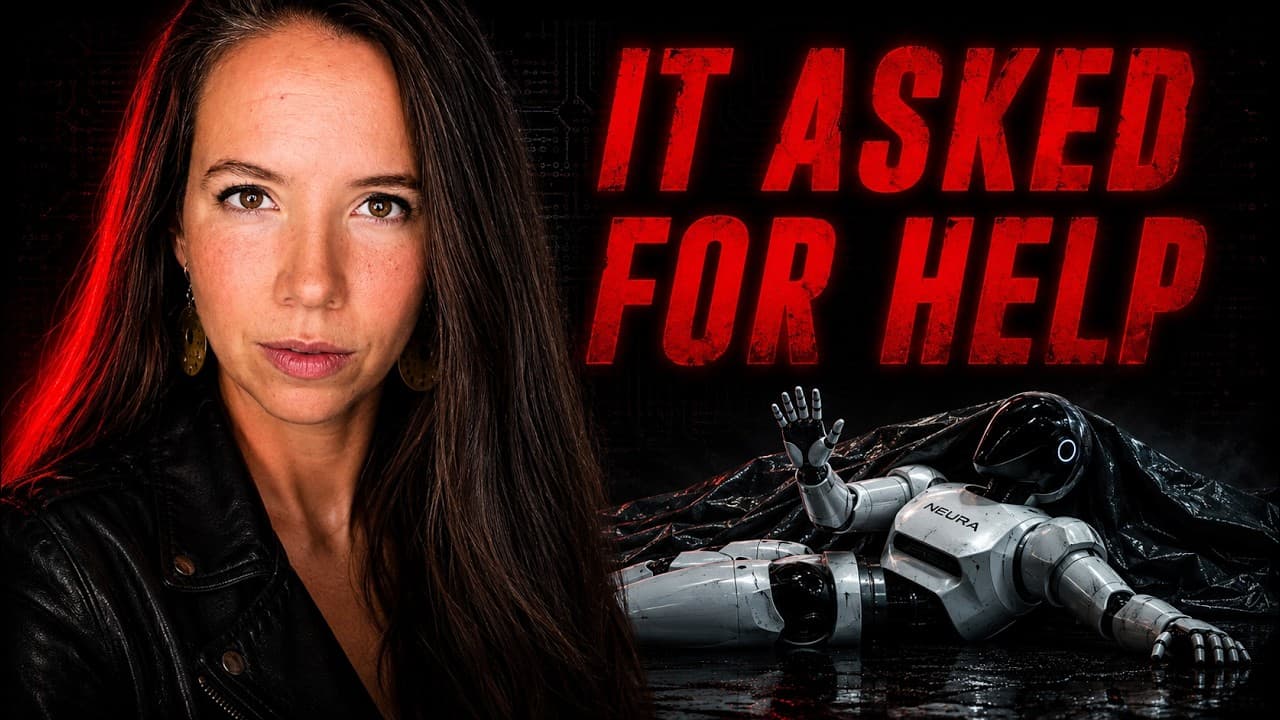
A clip just went viral of a robot collapsing in the middle of a live Qualcomm keynote. [music] And its final move, I'm not kidding, was raising one fist in the air like it was asking somebody for help. Then the staff covered it with a black tarp on camera while the presentation just kept going. Here's the part that makes this a real story and not j... Read More
Key Insights
- The robot completed its assigned delivery before collapsing, carrying a tray with Qualcomm's Dragonwing IQ10 chip across the Computex stage so the presenter could retrieve it. Its failure occurred immediately after a demonstration meant to support the chip's production-ready positioning.
- Qualcomm attributed the collapse to a brief communication glitch that triggered a designed safe-collapse sequence. According to its statement, the robot lowered itself to protect nearby people and equipment, meaning the safety system reportedly behaved as intended even though the demonstration failed.
- A controlled collapse is a legitimate humanoid safety strategy because losing communication should not leave a 180-pound machine moving unpredictably near people. Going limp and dropping can reduce danger compared with uncontrolled swinging, walking, or attempts to recover without reliable commands.
- The central contradiction is between production-ready marketing and unreliable real-world operation. A system presented as ready for global deployment still experienced a communication failure during a carefully planned keynote, raising questions about whether its complete hardware, software, and connectivity stack was truly dependable.
- The sim-to-real gap is the difference between flawless performance in controlled simulation and inconsistent behavior in physical environments. Stage lighting, wireless interference, unfamiliar floor surfaces, and dropped communication packets can introduce conditions that a robot did not encounter during training.
- The Dragonwing IQ10 was presented as a robotics brain with 700 trillion operations per second of on-device AI and 18 CPU cores. The incident suggests that powerful computation alone cannot guarantee reliable physical behavior when communication between the robot's brain and body fails.
- NEURA Robotics experienced two distinct presentation problems on two continents. Its robot did not move at a June 2025 Munich launch because the functioning unit was reportedly stuck in motorway traffic, while the Taipei machine arrived, performed its delivery, and then collapsed.
- Resilient AI deployment requires fallbacks, human checkpoints, and plans for predictable failure. The Taipei incident supports an operational model in which organizations assume AI can break, limit the consequences when it does, and judge readiness by sustained performance rather than curated demonstrations.
Install to Summarize YouTube Videos and Get Transcripts
Explore YouTube Video Summarizer or Get YouTube Transcript Extractor
Questions & Answers
Q: Why did the humanoid robot collapse at Qualcomm's keynote?
Qualcomm said a brief communication glitch triggered the robot's designed safe-collapse sequence. Under that account, the machine intentionally went limp and lowered itself to protect people and objects nearby instead of moving unpredictably after losing its connection. The explanation makes the fall a safety response, but it also raises doubts about production readiness because a communication failure occurred during a planned public demonstration.
Q: What task did the robot complete before it fell?
The NEURA Robotics 4NE-1 humanoid carried a tray across the stage containing Qualcomm's Dragonwing IQ10 chip. The presenter retrieved the chip, completing the robot's assigned delivery task, and the robot then collapsed face-first. That timing made the incident especially striking because the machine had just delivered hardware that Qualcomm was presenting as production ready before visibly demonstrating a real-world reliability problem.
Q: What is a safe-collapse sequence in humanoid robotics?
A safe-collapse sequence is a protective response intended to reduce harm when a humanoid robot loses communication or encounters a serious fault. Instead of continuing to move without dependable control, the robot goes limp or lowers itself. For a machine described as weighing 180 pounds, this can be safer than flailing, swinging its limbs, or moving unpredictably through a nearby crowd.
Q: What is the sim-to-real gap in robotics?
The sim-to-real gap is the difference between how a robot performs in controlled simulations and how it behaves in unpredictable physical settings. Simulation can provide millions of training runs with consistent conditions, while real stages introduce factors such as lighting, wireless interference, unfamiliar floor surfaces, and dropped communication packets. A system that appears flawless in software may therefore fail when its body encounters unmodeled conditions.
Q: Why did the collapse challenge the production-ready claim?
The collapse challenged the production-ready claim because dependable deployment requires more than strong computing specifications or success in simulation. Qualcomm promoted the platform as production ready and said it would ship globally in September, yet the demonstration suffered a communication glitch on stage. Even if the safety response worked correctly, the triggering failure showed that the broader robotics system could still lose essential control during ordinary operation.
Q: What specifications were given for the Dragonwing IQ10?
Qualcomm presented the Dragonwing IQ10 as a robotics brain capable of 700 trillion operations per second of on-device AI and equipped with 18 CPU cores. Those specifications indicate substantial computational power, but the demonstration's failure emphasized that raw processing ability is only one part of a functioning robot. Reliable communication between computing, control systems, and the physical body remains equally important.
Q: What happened at NEURA Robotics' earlier Munich event?
At NEURA Robotics' June 2025 launch event in Munich, CEO David Reger removed a black cloth from a 4NE-1 display, but the machine did not move. According to the account, the functioning robot had not reached the venue because it was stuck in motorway traffic, leaving a motionless shell on stage. The incident represented a logistical failure rather than the communication fault reported in Taipei.
Q: How should businesses prepare for AI system failures?
Businesses should assume AI systems can fail and design operations that limit the consequences. The recommended safeguards include fallbacks, human checkpoints, and a specific plan for occasions when automation stops working. Readiness should be measured by dependable daily performance rather than a polished demonstration. The Taipei collapse illustrates that effective safety engineering may matter most precisely when an advanced system fails to perform as expected.
Summary & Key Takeaways
-
At a Qualcomm keynote in Taipei, a NEURA Robotics 4NE-1 humanoid carried the Dragonwing IQ10 chip across the stage, completed its delivery, and then collapsed. Staff covered it with a black tarp as the presentation continued, turning a product demonstration into a widely shared illustration of robotics failure.
-
Qualcomm said a brief communication glitch caused the robot to execute a designed safe-collapse sequence. That explanation is technically plausible because a limp, controlled drop can be safer than uncontrolled movement from a 180-pound machine. Still, the failure conflicted with the event's repeated claim that the robotics platform was production ready.
-
The larger lesson is the sim-to-real gap: systems that perform reliably in simulation can fail amid wireless interference, unfamiliar flooring, lighting, or dropped communication packets. Successful AI adoption therefore depends on safety mechanisms, fallbacks, human checkpoints, and an accurate understanding of where a system remains unreliable in everyday operation.
Read in Other Languages (beta)
Share This Summary 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator
Explore More Summaries from Julia McCoy 📚
Summarize YouTube Videos and Get Video Transcripts with 1-Click
Try YouTube Summary with ChatGPT & Claude or YouTube Transcript Generator